Orca-AI-Incident-Archive
Health Warn
- License — License: NOASSERTION
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Low visibility — Only 5 GitHub stars
Code Pass
- Code scan — Scanned 12 files during light audit, no dangerous patterns found
Permissions Pass
- Permissions — No dangerous permissions requested
No AI report is available for this listing yet.
An open database of real-world AI agent incidents.
Orca AI Incident Archive
An open database of real-world AI agent incidents
English · 简体中文 · 日本語 · 한국어 · Deutsch · Français · Español


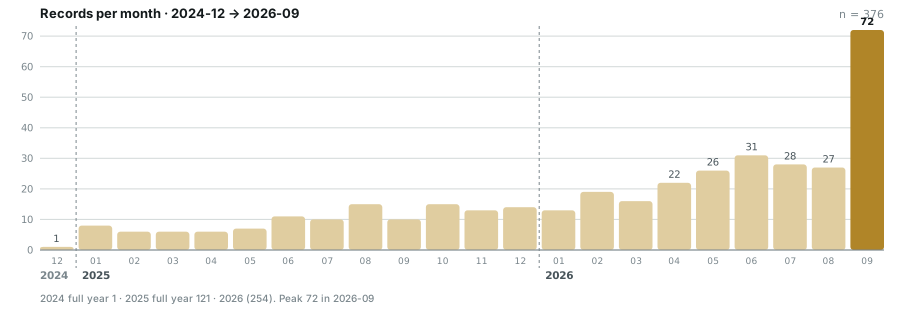
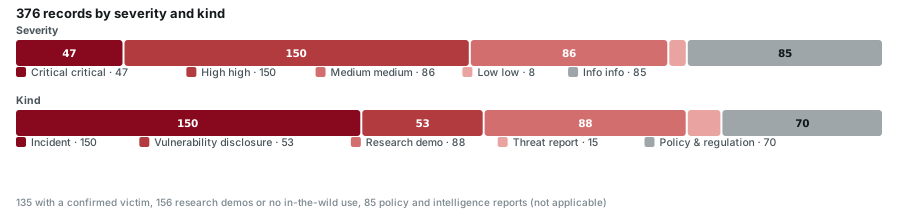
Coverage runs from 2025-01 to 2026-09-24 — 371 records of AI agent security events arranged month by month, plus one precursor traceable to 2024-12-01. Each record is a single Markdown file with a YAML header, an attack-chain diagram and at least one primary source you can click. Of the 371, only 134 have a confirmed victim.
This archive exists for one distinction that most incident lists collapse:
An agent that actually caused damage is not the same thing as a researcher showing that it could.
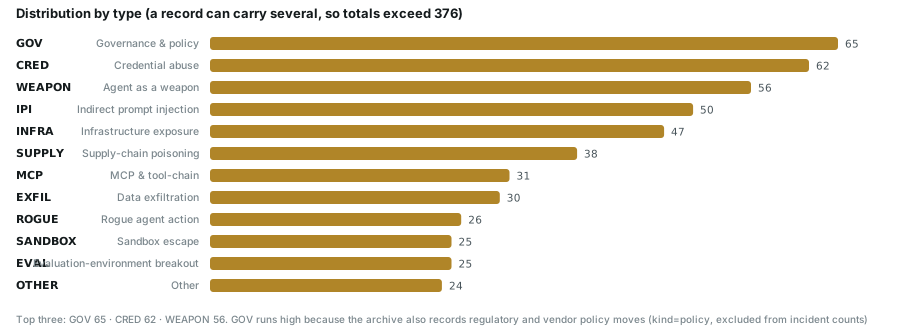
Every record answers three questions before anything else — was there a confirmed victim (real_harm), was the AI involvement confirmed by a primary source (ai_involvement), and is this an incident, a vulnerability disclosure, a research demo, a threat report or a policy move (kind). Without those three fields, "300+ AI incidents this year" is a number that means nothing.
At a glance
Where to start
| I want to… | Go here |
|---|---|
| Read it chronologically | All records by month |
| See only what actually happened | The critical list · or filter real_harm: true |
| Read by attack surface | Seven topics |
| Look at one country or region | Regional slices |
| Understand the fields | SCHEMA.md · Taxonomy · Docs |
| Analyse the data | dist/ — JSON, CSV, stats, every source URL |
| Browse interactively | index.html — one file, works offline, seven languages |
[!NOTE]
Language. Records are written in English. Titles and summaries are available in seven languages (English, Chinese, Japanese, Korean, German, French, Spanish); the complete Chinese text of every record lives underincidents/i18n/zh/. Cited sources stay in their original language. Further translations are welcome; see CONTRIBUTING.md.
By month
2024 (1 records)
| 12 |
|---|
1 |
2025 (121 records)
| 01 | 02 | 03 | 04 | 05 | 06 | 07 | 08 | 09 | 10 | 11 | 12 |
|---|---|---|---|---|---|---|---|---|---|---|---|
8 ★1 |
6 |
6 |
6 |
7 |
11 |
10 ★2 |
15 ★2 |
10 ★1 |
15 |
13 ★3 |
14 |
2026 (249 records)
| 01 | 02 | 03 | 04 | 05 | 06 | 07 | 08 | 09 |
|---|---|---|---|---|---|---|---|---|
13 ★1 |
19 ★5 |
16 ★3 |
22 ★2 |
26 ★5 |
31 ★3 |
28 ★7 |
27 ★4 |
67 ★8 |
n = records that month, ★ = of which critical
Critical
Any of three triggers: ① confirmed damage reaching multiple organisations, a government, critical infrastructure or a supply-chain worm; ② a first-of-its-kind capability milestone with real victims; ③ research that overturns a widely deployed defence — real_harm: false in that case, 2 of these. Full criteria in taxonomy/severity.md.
What counts as a record
A record qualifies if at least one of these is true:
- The AI agent was the one carrying out the attack — autonomously or driven by a human
- The AI agent was the target — injection, poisoning, escape, exposed infrastructure
- The AI agent was a link in the damage chain — it read hostile content and acted on it
- It is a regulatory, legislative or vendor action directly about agent security (recorded as
kind: policy, not counted as an incident)
Out of scope: pure LLM content-safety findings (jailbreaking a model into saying something it shouldn't), ordinary vulnerabilities unrelated to agents, and claims with no traceable primary source.
Two categories are labelled rather than deleted:
ai_involvement: unverified— widely reported as an AI incident, but the primary source contains no AI. Kept so the claim is searchable together with its rebuttal.ai_involvement: disputed— the vendor and the reporting disagree; both accounts are preserved side by side in the record.
Full criteria: docs/scope.md.
Data quality
| Source links | 715 links across 645 unique URLs |
| Records with no source | 0 — no source, no entry |
| Grade A (primary source) | 317 |
| Flagged as disputed | 14 |
| Verification rounds | 4 |
The first three rounds checked every record individually. The fourth round did a coverage audit and still found roughly 11% missing. These catch entirely different problems: "is what we have correct" and "is what we should have here" are separate questions and have to be asked separately.
Those four rounds deleted two fabricated entries, corrected PaperCut's "domain admin in six hours" to seven minutes, and downgraded Step Finance to grade D because the primary reporting never mentions AI at all. Every correction is recorded in docs/data-quality.md — nothing was silently overwritten.
Cite
@misc{orca_ai_incident_archive,
  title  = {Orca AI Incident Archive: An open database of real-world AI agent incidents},
  year   = {2026},
  note   = {371 records, 2025-01 to 2026-09; 134 with confirmed real-world harm},
  url    = {https://github.com/Continuum-AI-Corp/Orca-AI-Incident-Archive}
}
When citing a single record, use its id — for example orca:2026-07-09-openai-agents-breach-huggingface.
Contribute
Corrections, missing records and better sources are all welcome. Three hard rules:
- Every record needs a primary source you can click. No source, no merge.
- If you are unsure, label it — do not delete it. Disputed facts get
disputed: trueand both accounts stay in the record. - Corrections go into the record, never silently over it. Say what changed and why.
See CONTRIBUTING.md. Issue templates for a new record and a correction are set up.
Licence and disclaimer
Licensed CC BY 4.0 — attribution required. Linked source material remains the copyright of its respective owners.
This archive records only publicly disclosed events. It contains no undisclosed vulnerability detail, no exploit code and no attack tooling. Classification and severity are the editors' judgement, not an official finding by any vendor or regulator. If you are an affected party and believe a record is wrong, open an issue — it will be checked and corrected.
Built 2026-09-24 · 371 records · 22 months · Structure: SCHEMA.md · Data: dist/
Reviews (0)
Sign in to leave a review.
Leave a reviewNo results found