kanareika
mcp
Warn
Health Warn
- License — License: MIT
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Low visibility — Only 6 GitHub stars
Code Pass
- Code scan — Scanned 12 files during light audit, no dangerous patterns found
Permissions Pass
- Permissions — No dangerous permissions requested
No AI report is available for this listing yet.
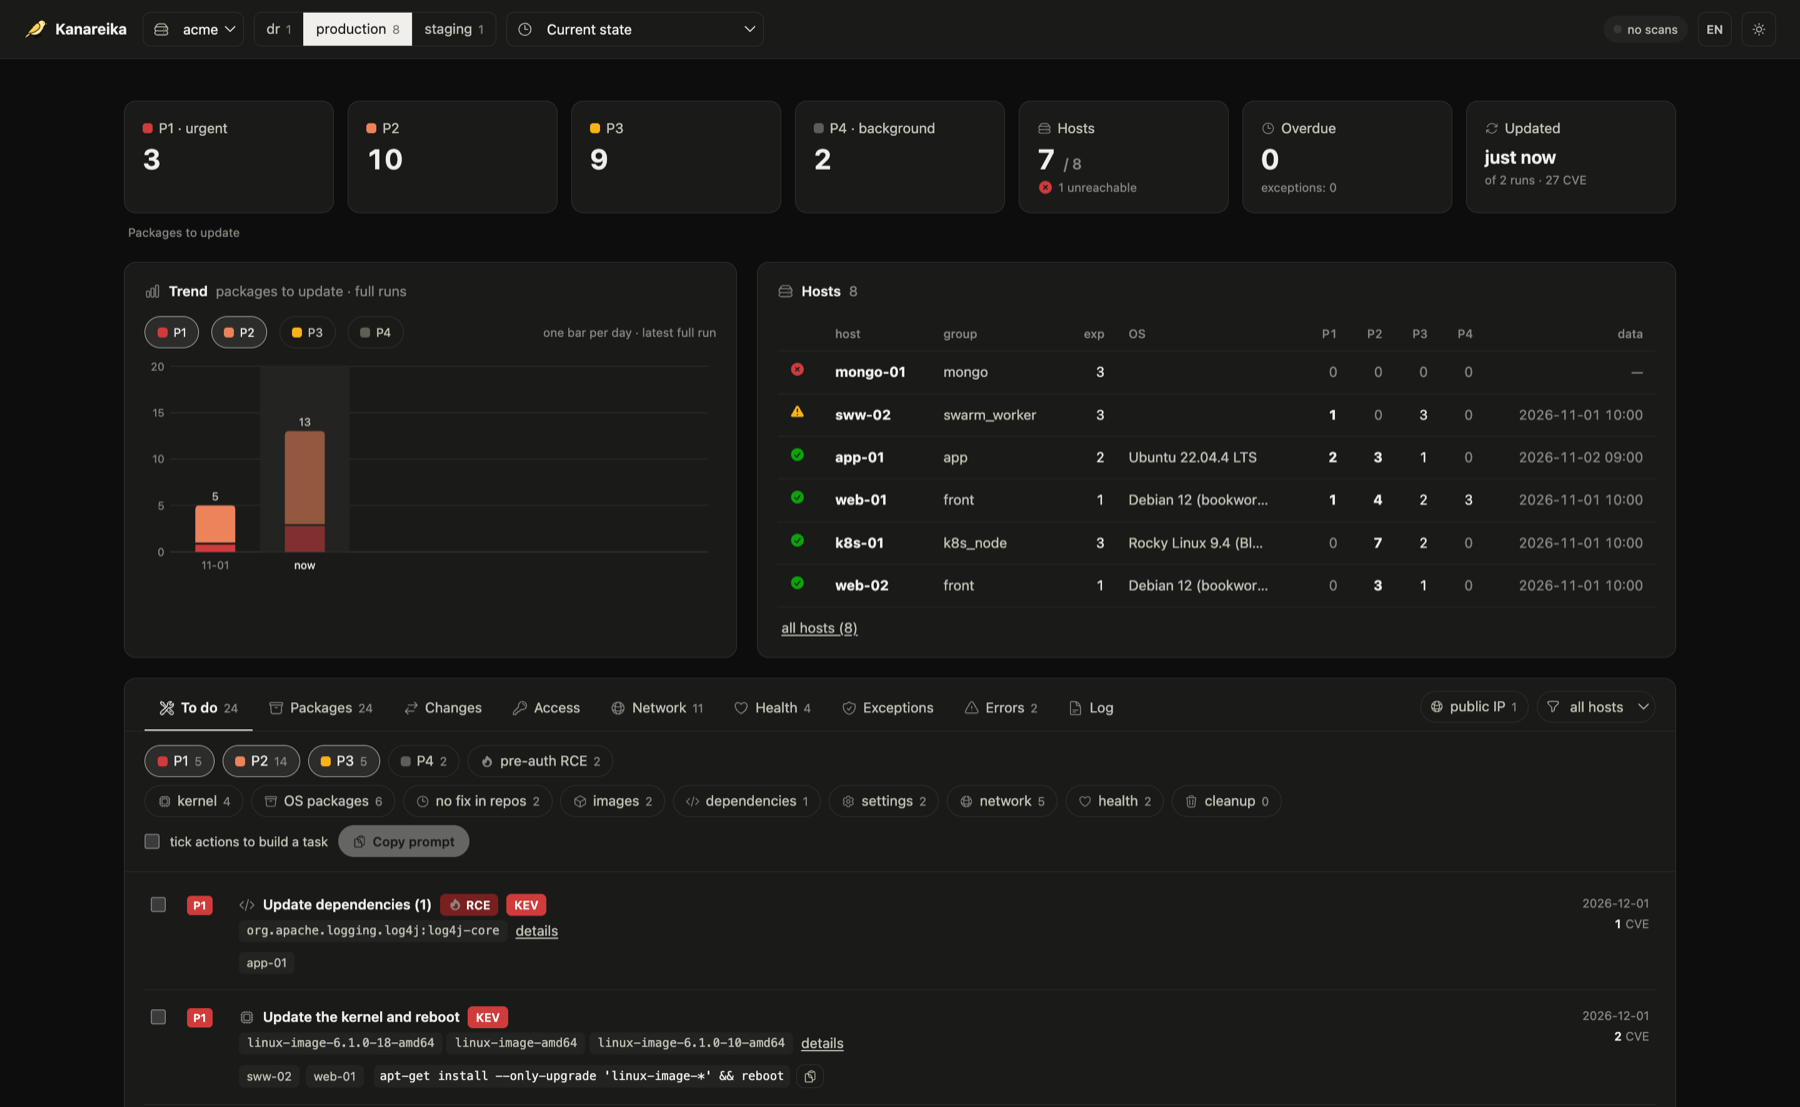
Agentless, read-only Linux server security audit over SSH: vulnerability scanning (CVE, Trivy, KEV, EPSS), patch prioritization, SSH access & exposure checks, host health. Single Go binary with dashboard and MCP server for AI agents.
README.md
Kanareika


English · Русский
Agentless, read-only security audit of your servers over SSH: what to patch first, who can get in, what is exposed,
whether the host is healthy — with rollback-ready fix steps. One binary, one YAML per organization, data stays local.
make bin                     # or download kanareika-<os>-<arch> from the release
make new-org ORG=myorg       # describe hosts, jump hosts and consent in orgs/myorg.yml
make feeds && make scan ORG=myorg
make dashboard               # http://127.0.0.1:8088
- Vulnerabilities — OS packages, images, jars/lockfiles via trivy (fetched automatically); backports and fix
availability verified on the host; P1–P4 by KEV, EPSS, exposure and pre-auth RCE. - Access & exposure — SSH password login per user, keys, logins and attackers, open ports, firewalls, external scan.
- Health — kernel errors, disks, memory, time sync, pending reboots.
- Fixing — pick actions → a ready task for an engineer or AI agent (apply / verify / rollback); MCP for agents.
- Safe by design — read-only, per-org isolation, changed host keys refused, consent required, localhost dashboard.
Details: docs/org-file.md · kanareika --help
License: MIT · Contributing · Security
Reviews (0)
Sign in to leave a review.
Leave a reviewNo results found