Keyfence
Health Warn
- License — License: MIT
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Low visibility — Only 5 GitHub stars
Code Warn
- crypto private key — Private key handling in bench/corpus.py
Permissions Pass
- Permissions — No dangerous permissions requested
No AI report is available for this listing yet.
Local proxy that keeps your API keys and secrets out of LLM requests. Works with Claude Code, Cursor, Codex and any tool.
keyfence


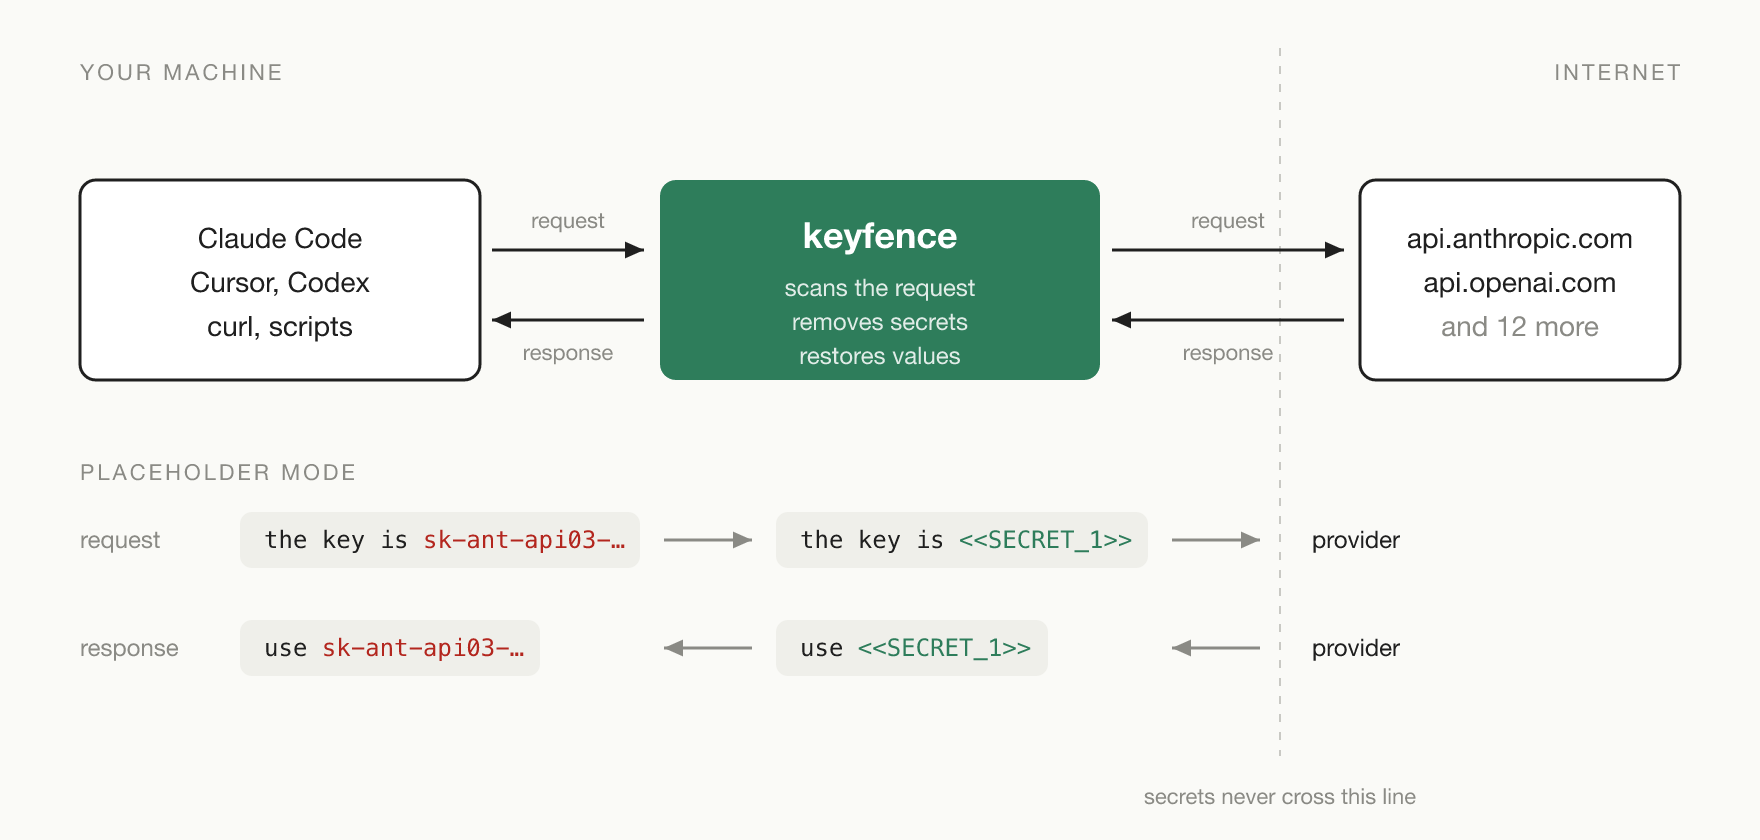
A local proxy that stops secrets from reaching LLM APIs. It checks every
request to an AI provider before it leaves your machine and blocks, redacts
or placeholder-swaps API keys, passwords and other secrets. Coding agents
read .env files and credential stores and send what they find to the
model; keyfence makes sure the values never arrive.
Try it in one minute
uv tool install keyfence     # or: pipx install keyfence, or pip install keyfence
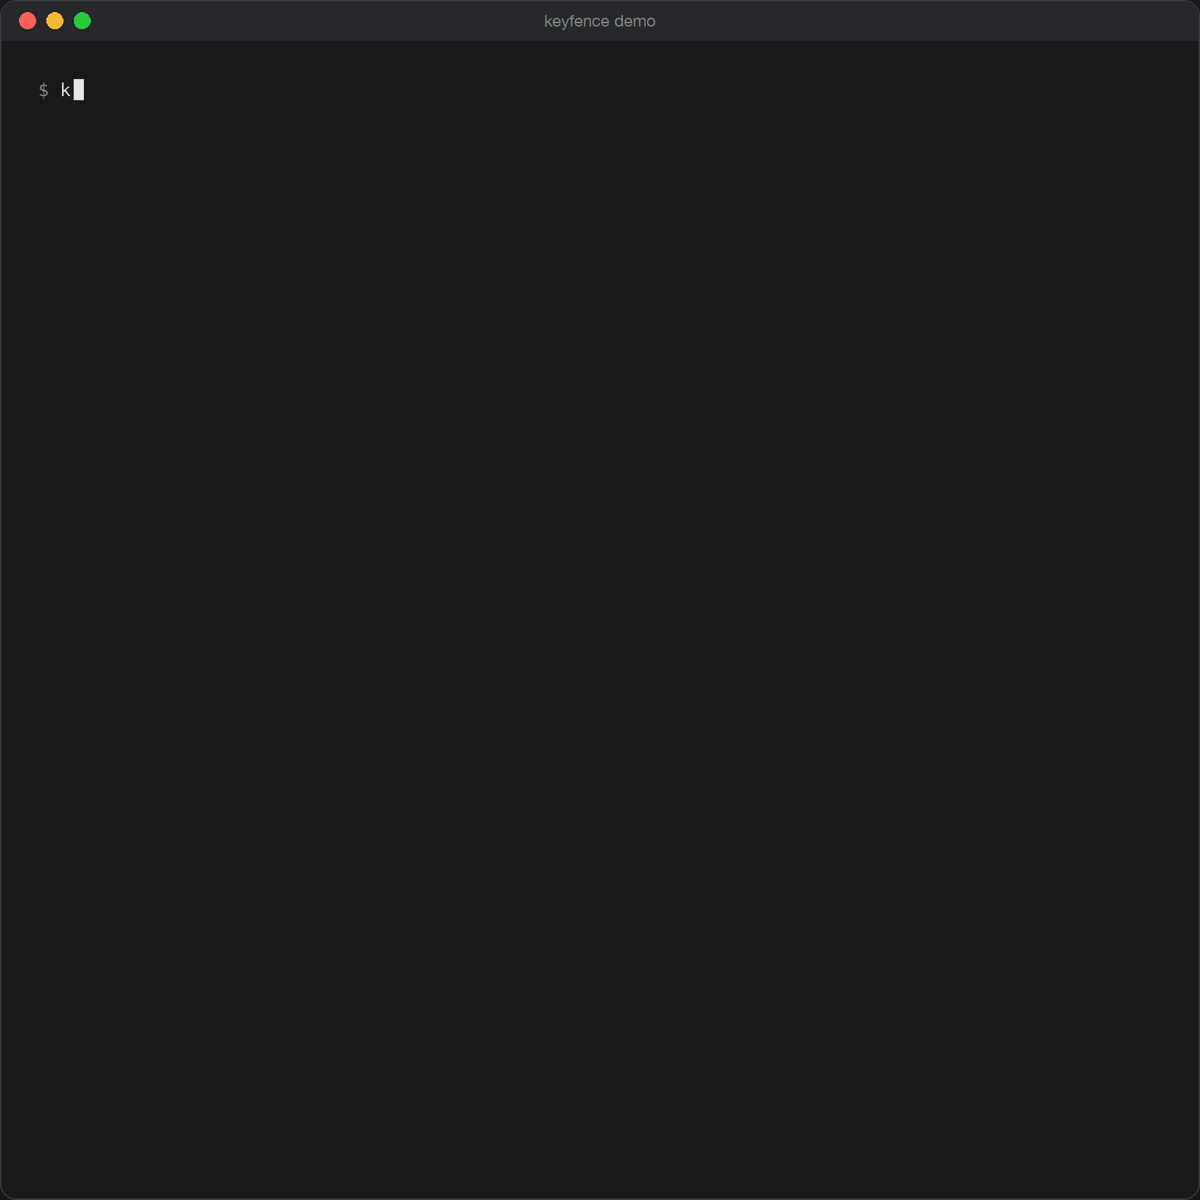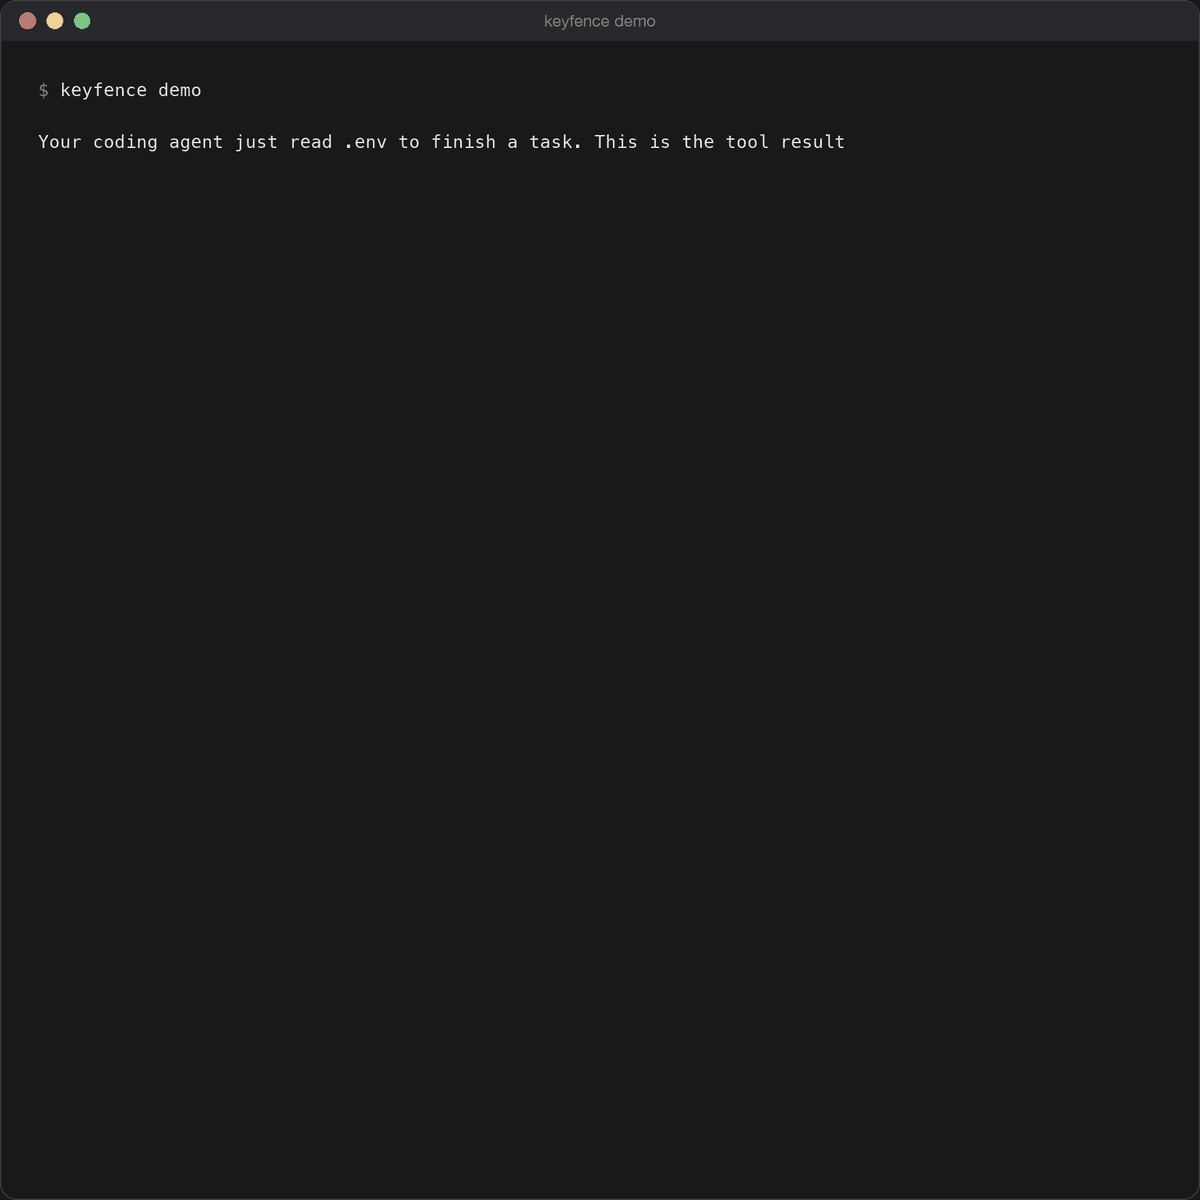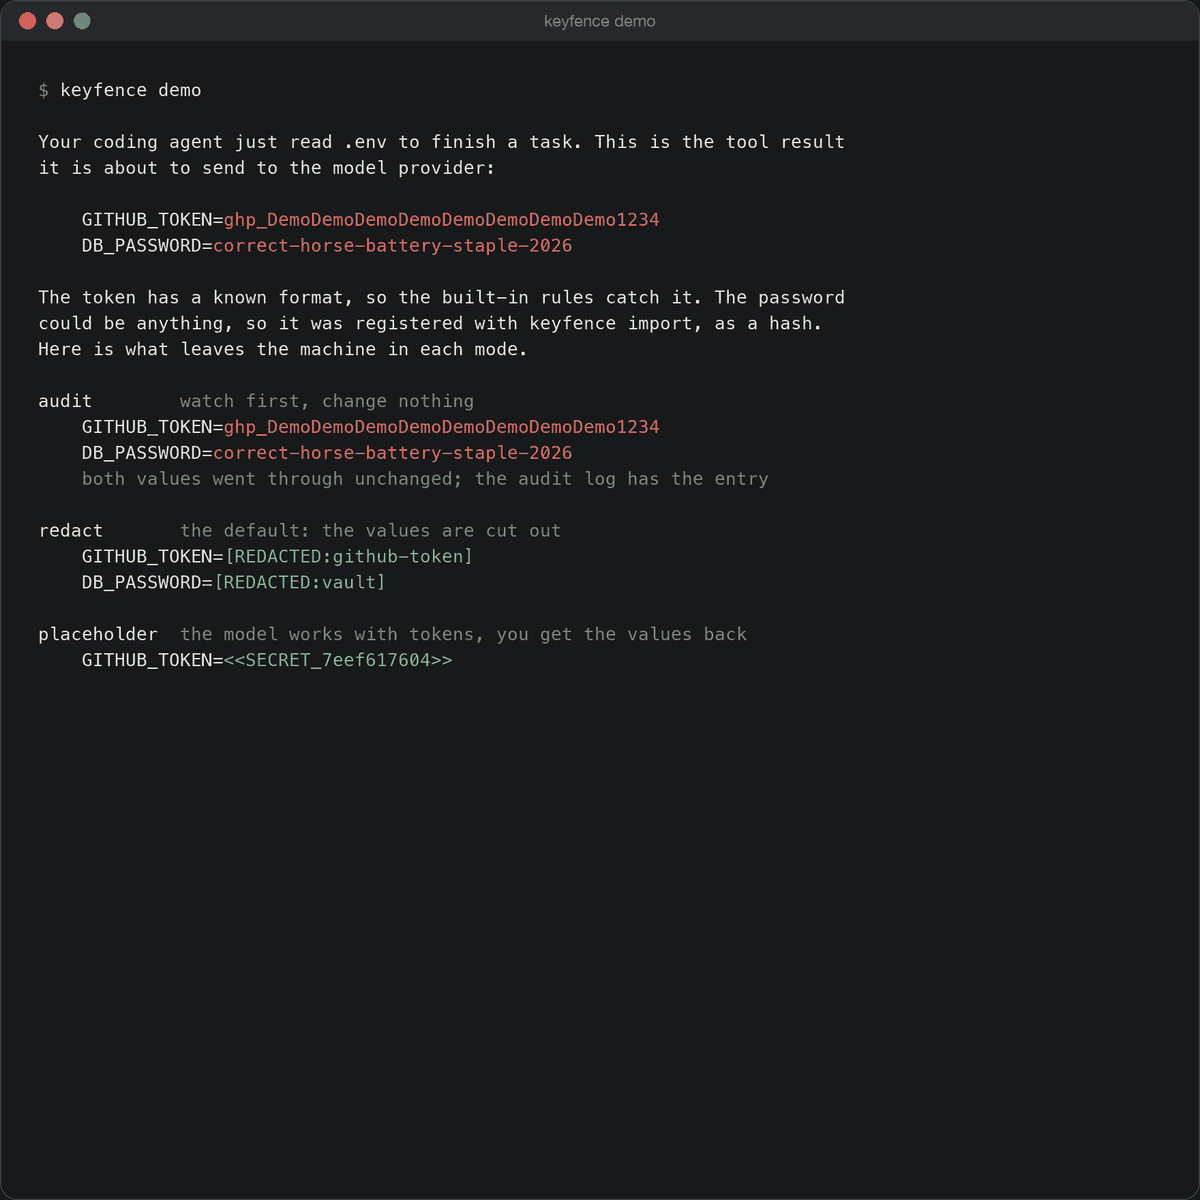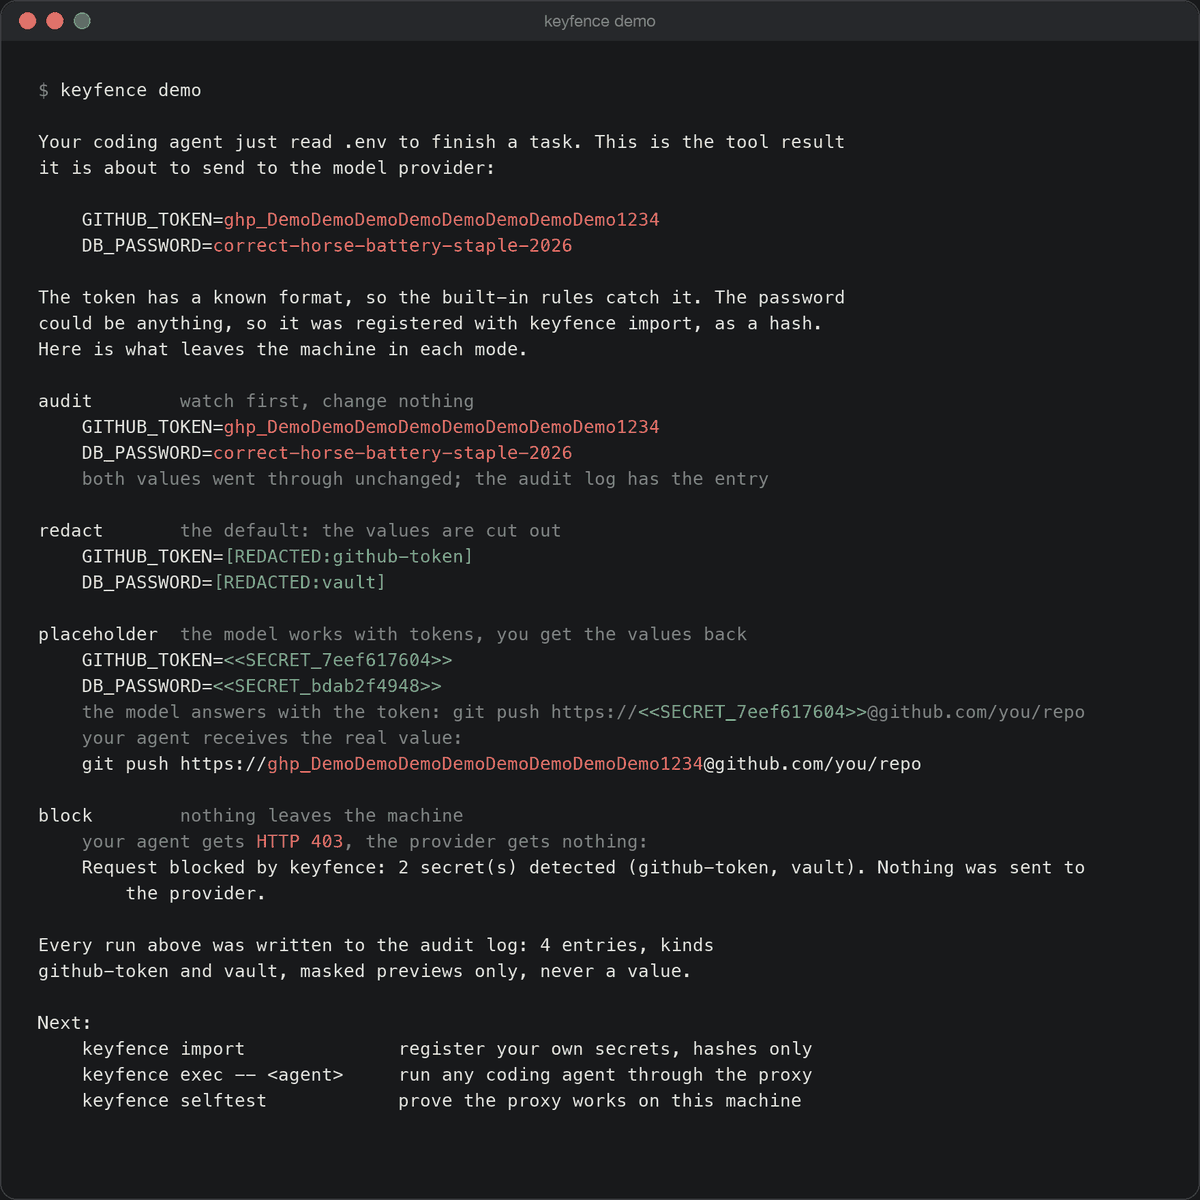
keyfence demo                # shows what each mode does to a fake request, no network
Use it
keyfence import              # register your own secrets: .env files and credential stores, hashes only
keyfence exec -- claude      # run Claude Code through the proxy
That is the whole setup for Claude Code, pi, Codex, Aider, curl and
anything built on the Python or Node SDKs: keyfence exec starts the
proxy, points the command at it and hands it the CA certificate, then
stops the proxy when the command exits. No sudo, nothing changes on
your system.
Not sure it is working? keyfence doctor checks every piece and says what
to fix; keyfence selftest sends a throwaway secret through a fresh proxy
and checks what comes out the other side. keyfence status shows what has
been caught.
Two more layers, both optional:
keyfence install-hooks claude-code   # Claude Code refuses to read secret files, and refuses a prompt that carries a secret
keyfence install-hooks pi            # same for pi, as a pi extension
keyfence canary .env                 # plant a fake secret; if a tool ever sends it, you will know
Modes
Set mode in ~/.keyfence/config.yaml.
| mode | behaviour |
|---|---|
audit |
log what would have been caught, change nothing; start here to see what your tools send |
redact (default) |
secret becomes [REDACTED:<kind>] |
placeholder |
secret becomes <<SECRET_id>> and the real value is restored in the response, streaming included |
block |
request gets a 403 and is not sent; a WebSocket text frame is dropped |
What it catches
Your own secrets, whatever their format, once registered withkeyfence import (from .env files, ~/.aws/credentials, ~/.netrc,~/.npmrc, ~/.docker/config.json, or --from op|vault|doppler|aws);
240 known formats through built-in rules and the bundled gitleaks ruleset;
and high-entropy strings that look like secrets. Only salted hashes are
stored. Details and numbers in the benchmark.
Verified with
Claude Code (through exec, --local and the hook), pi (through exec
and the extension), the Anthropic and OpenAI HTTP APIs, curl, Python and
Node clients. GitHub Copilot, Vertex AI and Azure AI hosts are on the
default list but have not been tested end to end. Cursor and Windsurf
route through their own backends and are not on the list; add their hosts
with extra_hosts if you want to try, and an issue with the result helps
either way.
Documentation
- Setup:
install options, GUI apps and system-wide trust, capturing tools that
ignore proxies, Docker, all commands. - Detection:
the vault, pattern rules, entropy check, what is excluded, the audit log. - Configuration:
every option, environment variables, the system prompt notice. - Benchmark:
recall by secret format and false positive rate by content type, against
gitleaks, reproducible withpython bench/run.py. - Limitations:
what keyfence does not cover and what to combine it with. - Claude Code plugin:
the hook and two skills, installable with/plugin marketplace add aminueza/keyfence. - Agents:
whatinstall-hooksdoes for Claude Code and for pi. - Agent hook contract:
the wire format ofkeyfence hook, the tool names and fields per agent,
and how to wire up another agent. - Security:
what the proxy sees, what it stores, how releases are built. - Development
and Changelog.
License
MIT. Bundled detection rules come from gitleaks,
also MIT.
Reviews (0)
Sign in to leave a review.
Leave a reviewNo results found