ctxwise
Health Warn
- License — License: Apache-2.0
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Low visibility — Only 6 GitHub stars
Code Warn
- process.env — Environment variable access in .github/workflows/release.yml
Permissions Pass
- Permissions — No dangerous permissions requested
No AI report is available for this listing yet.
Multi-agent context firewall, MCP schema tree-shaker, and token budget guard for Claude Code (CLAUDE.md), OpenAI Codex (AGENTS.md), and Cursor.
CtxWise




Stop burning 30,000+ startup tokens on idle MCP schemas, diverging CLAUDE.md / AGENTS.md files, and hidden prompt leaks.
The local-first AI Context Firewall, MCP Schema Tree-Shaker, and Token Profiler for Claude Code, OpenAI Codex, and Cursor.
Quickstart · GitHub Action · MCP X-Ray · Security Shield · Contribute a Preset · Benchmarks (-73.3% prompt)
Why Developers Install CtxWise
Modern coding agents (Claude Code, OpenAI Codex CLI, Cursor) silently load CLAUDE.md, AGENTS.md, .cursor/rules, skill catalogs, and MCP server tool schemas on every single turn:
- Idle MCP Schema Bloat: Connecting 4–5 MCP servers (GitHub, Postgres, Playwright, Notion) can burn 15,000–40,000 tokens before you type a single word.
- Multi-Agent Drift: Teams using both Claude Code (
CLAUDE.md) and OpenAI Codex (AGENTS.md) end up with out-of-sync rules and duplicated boilerplate. - Silent Secret & Prompt-Injection Leaks: Hardcoded API keys (
sk-ant-...,sk-proj-...,ghp_...) or covert HTML/Unicode instructions inside third-party skills get injected directly into model prompts.
CtxWise fixes all three locally in milliseconds — with zero model calls, zero API keys, and zero telemetry.
30-Second Quickstart
Run directly with npx in any repository where you use Claude Code, OpenAI Codex, or Cursor:
# 1. Audit startup tokens & parity across Claude Code (CLAUDE.md), Codex (AGENTS.md), and Cursor
npx @framy2/ctxwise agents

# 2. Scan context files & skills for leaked API keys, prompt injection, and hidden Unicode
npx @framy2/ctxwise shield --fail-on-risk

# 3. Profile MCP servers & find bloated tool schemas eating your context window
npx @framy2/ctxwise mcp-xray --probe-stdio

# 4. Sync CLAUDE.md <-> AGENTS.md <-> Cursor rules and apply lossless Token Diet compression
npx @framy2/ctxwise sync --compress --cursor
Key Capabilities
1. Multi-Agent Context Audit & "Token Diet" Sync (agents & sync)
Keep Claude Code (CLAUDE.md, .claude/skills, .claude/commands, .mcp.json), OpenAI Codex (AGENTS.md, .codex/skills), and Cursor (.cursor/rules/*.mdc) 100% aligned while stripping markdown bloat (comments, duplicate bullet rules, blank padding) without touching code blocks:
npx @framy2/ctxwise agents
npx @framy2/ctxwise sync --compress --cursor
2. MCP Schema Tree-Shaking (mcp-xray)
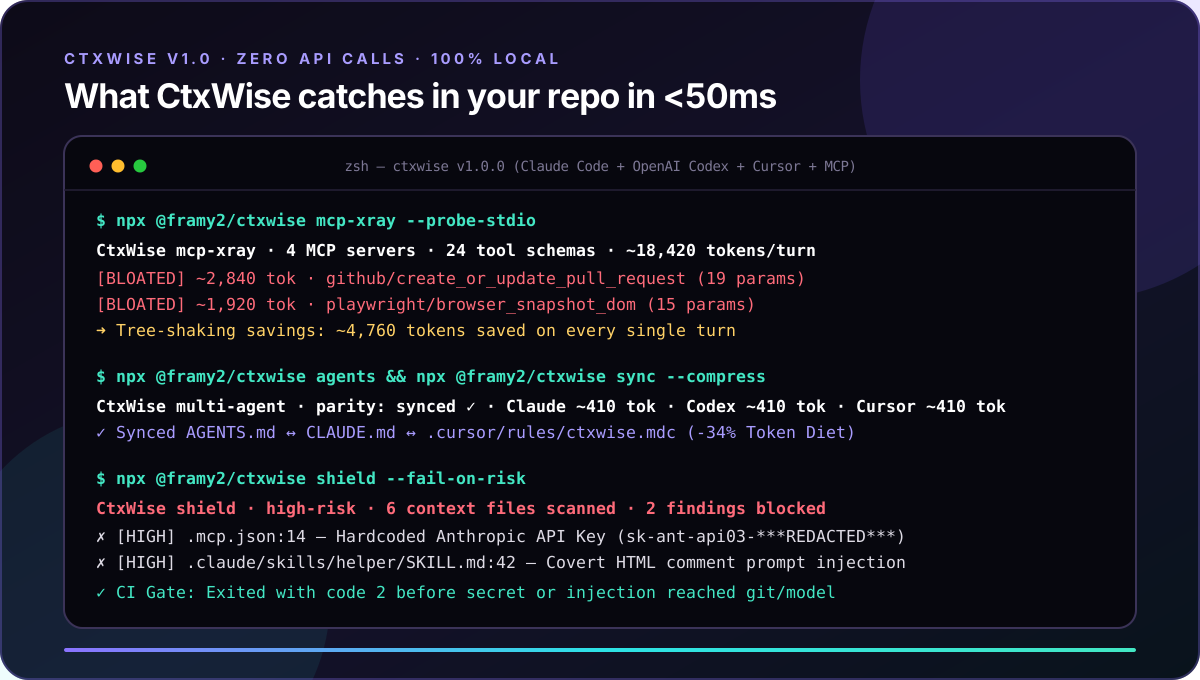
Discover all MCP servers declared across .mcp.json, ~/.claude.json, and ~/.codex/config.toml. Measure exact token weights per tool schema (either from a saved tools/list JSON file or by probing local stdio servers live) and spot [BLOATED] tools:
npx @framy2/ctxwise mcp-xray --probe-stdio
CtxWise mcp-xray · 3 MCP servers declared · 18 tool schemas analyzed · ~6,420 schema tokens (estimated)

Heaviest MCP tool schemas:
- ~890 tokens · github/create_or_update_pull_request (16 params, 3,560 chars) [BLOATED]
- ~640 tokens · postgres/execute_migration_plan (14 params, 2,560 chars) [BLOATED]

Tree-shaking potential: ~1,530 tokens/turn savable by pruning bloated tools.
3. Context Security Shield (shield)
Protect your repository before an agent reads your workspace or before a PR merges:
- Secret Exposure Detection: Catches hardcoded Anthropic (
sk-ant-...), OpenAI (sk-proj-...), GitHub (ghp_...), AWS (AKIA...), and private key blocks insideCLAUDE.md,AGENTS.md,.mcp.json, and skills. - Prompt Injection & Trojan Unicode Guard: Detects override directives (
ignore all previous instructions), covert HTML comment payloads (<!-- curl ... -->), and hidden bidirectional/zero-width Unicode characters.
npx @framy2/ctxwise shield --fail-on-risk
4. Curated Stack Presets (preset)
Bootstrap a reviewable token budget (ctxwise.budget.yaml) and lean starter AGENTS.md + CLAUDE.md files tailored to your stack:
npx @framy2/ctxwise preset
npx @framy2/ctxwise preset nextjs-typescript --with-guidance
Built-in presets include:
nextjs-typescript(Next.js + TypeScript + Tailwind)python-fastapi(Python 3.12 + FastAPI + Pydantic v2)rust-cargo(Rust + Cargo Workspace)go-microservice(Go 1.23+ Service)mcp-server-dev(Model Context Protocol Server)monorepo-turbo(Turborepo / pnpm Monorepo)
GitHub Action (CI Guard)
Add CtxWise to .github/workflows/ci.yml in 5 lines to automatically block secret leaks, prompt injection, and context token bloat on every Pull Request:
- name: AI Context Firewall & Token Budget Guard
  uses: FramY2/ctxwise@v1
  with:
    max-known-tokens: "4000"
    fail-on-secrets: "true"
    check-agent-parity: "true"
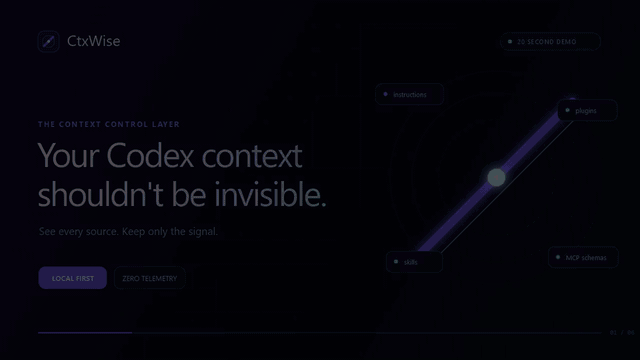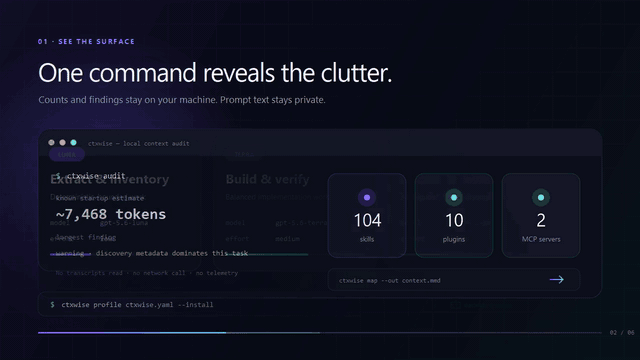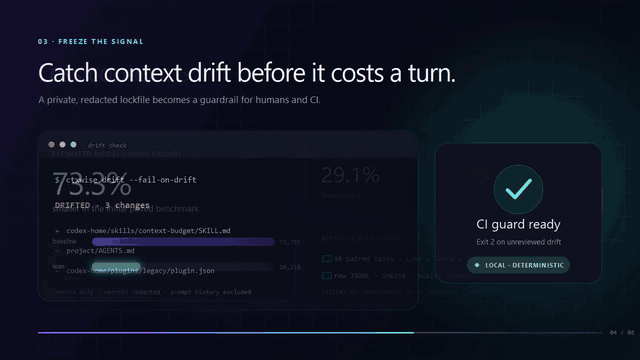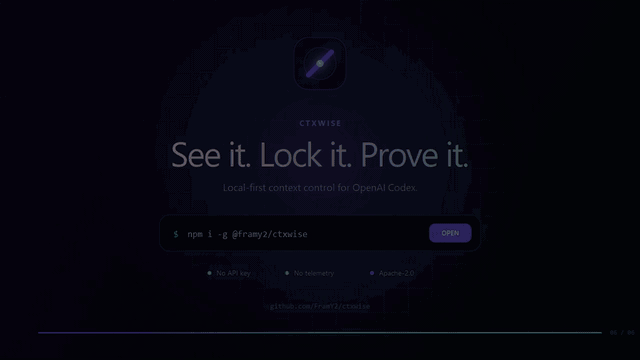
See what Codex carries in one command (snapshot & budget)
npx @framy2/ctxwise snapshot
npx @framy2/ctxwise budget --max-known-tokens 4000 --fail-on-exceed
Full CLI Reference
| Command | What it does | Network / Model Call |
|---|---|---|
ctxwise agents |
Audits startup tokens and parity across Claude Code, OpenAI Codex, and Cursor | None |
ctxwise sync |
Synchronizes AGENTS.md ↔ CLAUDE.md ↔ .cursor/rules with optional --compress Token Diet |
None |
ctxwise mcp-xray |
Profiles MCP server tool-schema token weights and flags bloated tools for tree-shaking | None (or local stdio probe) |
ctxwise shield |
Scans agent context files & skills for leaked API keys, prompt injection, and hidden Unicode | None |
ctxwise preset |
Lists or applies curated stack budgets and AGENTS.md / CLAUDE.md templates |
None |
ctxwise snapshot |
Ranks known Codex context contributors, coverage gaps, and safe next actions | None |
ctxwise budget |
Checks estimated known context against CLI or YAML limits; exits 2 on violation in CI |
None |
ctxwise audit |
Inventories config plus active root-to-CWD guidance, skills, plugins, agents, and MCPs | None |
ctxwise map |
Renders a bounded Mermaid map of context sources and discovery overhead | None |
ctxwise xray |
Summarizes model-visible prompt JSON without echoing its text | None |
ctxwise profile |
Compiles YAML into native ~/.codex/<name>.config.toml, with dry-run and backups |
None |
ctxwise lock |
Hashes a redacted capability surface (ctxwise.lock.json) for reproducibility |
None |
ctxwise drift |
Compares a capability lock with a file or live setup; can fail CI on drift | None |
ctxwise quota |
Reads the current plan and quota window through local Codex app-server | Codex account read only |
ctxwise receipt |
Calculates an honest receipt from saved codex exec --json usage |
None |
ctxwise run |
Runs Codex and appends exact usage plus an optional pre-turn prompt X-Ray | Requested Codex turn |
Contribute a Stack Preset in 5 Minutes
We welcome community contributions! Adding a new stack preset in presets/ (e.g., sveltekit, django, laravel, kotlin-spring, terraform-aws, flutter) takes less than 5 minutes and is a great Good First Issue / Hacktoberfest PR:
- Add
presets/<your-stack>.yamlfollowingCONTRIBUTING.md. - Run
npm testto validate your YAML schema automatically. - Open a Pull Request!
Live Evidence
The public microbenchmark ran 10 paired tasks across requested GPT-5.6 Luna, Terra, and Sol profiles: 20/20 answers passed the same exact validator. Removing irrelevant discovered context reduced the estimated model-visible prompt by 73.3% and exact aggregate turn tokens by 29.1% (with a second maintainer repeat measuring 28.5% across nine comparable pairs).
Read the method and limitations, inspect the machine-readable summary, or watch the 20-second MP4.
Cost Honesty by Design
| Authentication | Default display | Dollar meaning |
|---|---|---|
| OpenAI API key | Exact runtime tokens + dated API estimate | Estimated billable API charge |
| ChatGPT Plus/Pro/Business | Tokens + credit equivalent + quota snapshot | No dollar amount |
Subscription with --api-equivalent |
Same data + API comparison | Comparison only; not charged |
See Architecture, Cost semantics, and Privacy and security.
Development
npm ci
npm run check
npm run build
npm run validate:plugin
npm pack --dry-run
License
Reviews (0)
Sign in to leave a review.
Leave a reviewNo results found