CVEngine
Health Gecti
- License — License: GPL-3.0
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Community trust — 14 GitHub stars
Code Gecti
- Code scan — Scanned 12 files during light audit, no dangerous patterns found
Permissions Gecti
- Permissions — No dangerous permissions requested
Bu listing icin henuz AI raporu yok.
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
The most advanced external attack surface assessment you can get for free.
cvENGINE automatically discovers and maps your internet-facing assets, fingerprints every service and version it finds, and tells you which of today's exploited CVEs actually hit you, then reproduces what it can with safe, read-only checks. Enterprise-grade attack surface management with no license fee, no per-asset pricing, and fully opensource.



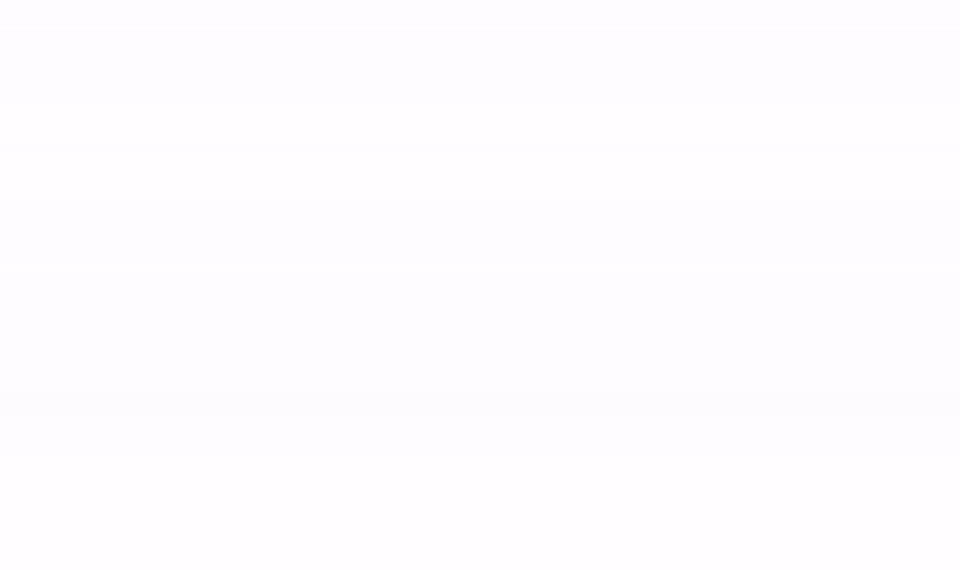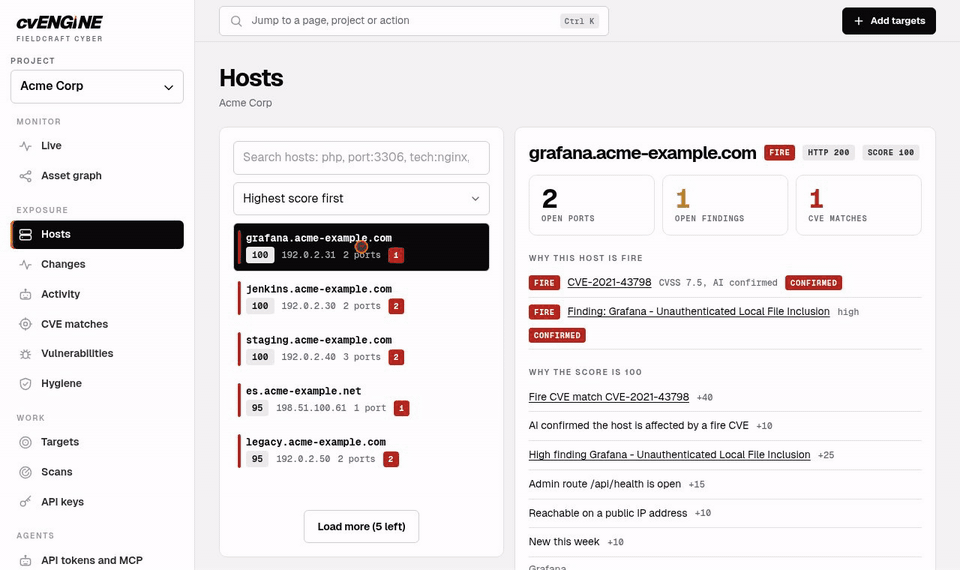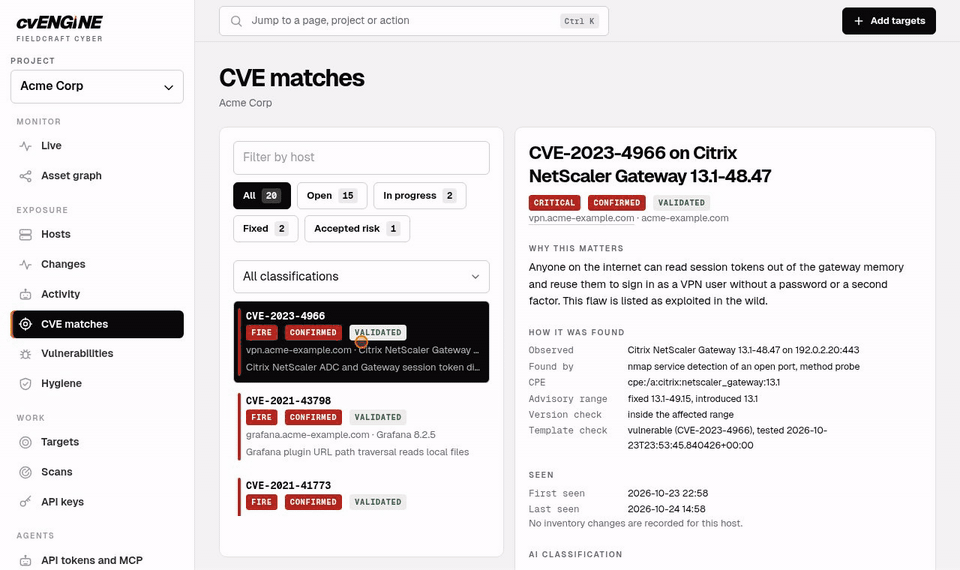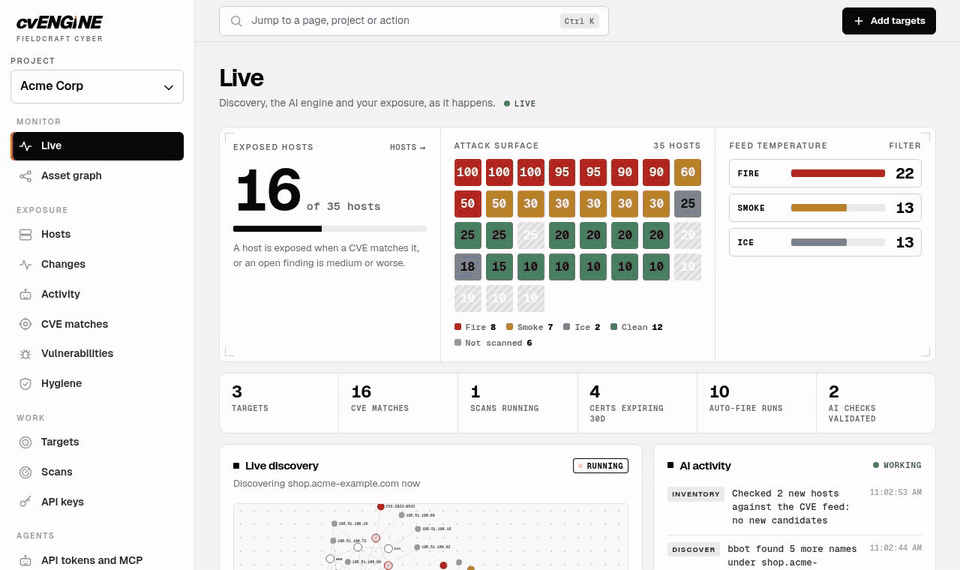
Why cvENGINE
Attack surface tools find assets. Vulnerability scanners find flaws. Threat feeds find CVEs. cvENGINE runs all three as one continuous loop and hands you a verdict instead of a pile of alerts. It answers the one question that matters: which of today's vulnerabilities are live on assets I own, and can I reproduce them?
- Total visibility. Domains, subdomains, IPs, ports, products, versions, TLS, and technologies are auto-discovered and stored in one Shodan-style inventory that keeps itself current. Just enter your domain name and cvENGINE does the rest.
- Matched to your environment. The live cve.now feed and the major exploitation sources are rated fire, smoke, or ice and matched to what you actually run, by product and version, with distribution backports understood.
- Verdicts, not noise. AI triages your findings, read-only checks reproduce what they can, and fixed rules mean the model can never wave away hard evidence. Every check records exactly what it ran.
- Nothing changes unseen. New hosts, opened ports, version bumps, new certificates, login pages that appear, and front pages that change all land on a timeline.
- Scanning in minutes. One Docker Compose stack with every scanner built in. No agents to install, no cloud account to open.
- Yours, completely. Open source and self-hosted. Your inventory stays on your server, and you bring your own AI keys or run a model on your own hardware. Nothing is sent to the authors.
Everything in the box
Discover. bbot subdomain and asset discovery in passive, standard, and deep modes (screenshots in deep). A certificate transparency watch that pulls new hostnames straight into assessment. Targets as domains, IPs, CIDR ranges, or URLs, bulk added by organization and project. Every apex domain gets a deep sweep each week.
Understand. One record per host: ports, services, products, versions, OS, banners, TLS, and technologies, from nmap and nuclei. A background sweep of all 65,535 ports, one host at a time, plus optional naabu. Web route checks that label each route open, login, session required, SSO, or redirect. Exposure checks for Redis, Memcached, PostgreSQL, Elasticsearch, and CouchDB that answer without a login. Email and domain hygiene: SPF, DKIM, DMARC, CAA, MTA-STS, DANE, DNSSEC, and TLS.
Prioritize. Fire, smoke, and ice ratings from CISA KEV, ENISA EUVD, Metasploit, Exploit-DB, EPSS, CVSS, and optionally VulnCheck KEV. A 0 to 100 score for every host, with the reasons shown. AI triage of every finding into confirmed, likely, needs validation, likely false positive, or not applicable. Connect your own AI, with your own API keys (Anthropic, OpenAI, OpenRouter) or a model on your own hardware (Ollama, vLLM), and a review every three hours queues the next triage, validation, or rescan per project and tunes scanner concurrency from real measurements.
Verify. Automatic read-only validation: a vetted nuclei template, a single-port nmap check, a banner probe, or the database check, each recording the exact command it ran. Validate now on any CVE match. When no template exists, the AI drafts one, and it never runs on your hosts until a person approves it. Optional auto-fire (off by default) tests new CVEs on matching hosts as the feed delivers them.
Operate. A live dashboard, an AI activity log, and a Changes page with side-by-side screenshot diffs. Rescan, pin, exclude, or archive any host, and record its owner and criticality. Organizations, projects, roles (admin, user, audit), an All projects view, two-step sign-in, an IP allowlist, and an audit log. A REST API, an MCP server, and an OpenAPI spec so agents work under the same permissions. A bug bounty workbench for hunters: browse HackerOne, Bugcrowd, Intigriti, and YesWeHack programs and scope, point the scanner at what is in scope, and draft reports from its findings. Off until an admin enables it. Slack, Discord, Telegram, and Lark alerts if you don't want to monitor a dashboard. One switch pauses all scanning. Memory-aware scheduling keeps small servers healthy, and updates drain running work first or deploy automatically on every new commit.
Bring your own AI. Anthropic, OpenAI, OpenRouter, Ollama, or vLLM, with keys stored encrypted. Without a model, cvENGINE still discovers, scans, matches CVEs, and validates findings. The AI adds triage, targeted scans, and template drafts.
Built on the best
cvENGINE stands on excellent open source work. Full credits and licenses are in THIRD-PARTY.md.
| Scanners | bbot discovery, nuclei and its templates, nmap, naabu, gowitness screenshots |
| Exploitation intelligence | CVE feed cve.now, CISA KEV, ENISA EUVD, FIRST EPSS, Exploit-DB, Metasploit, VulnCheck KEV, CVE List V5 |
| Backport and certificate data | OSV, Debian security tracker, crt.sh |
| Email security checks | adapted from MailFail |
| Bug bounty data | bounty-targets-data, Bugcrowd VRT |
| AI | Anthropic, OpenAI, OpenRouter, Ollama, vLLM, over the Model Context Protocol |
| Platform | Django, Celery, PostgreSQL, Redis, nginx, Gunicorn, WeasyPrint, VivaGraphJS, Geist |
How it works
Add a target and cvENGINE runs one pipeline for it. Each scanner runs once per host inside a time window, so repeat scans stay fast.
flowchart LR
T(["Add a target<br/>domain, IP, CIDR, URL"])
subgraph FIND["1 FIND"]
direction TB
D["Discovery<br/>bbot"] --> I["Inventory<br/>nmap, naabu"]
end
subgraph PROBE["2 PROBE"]
direction TB
X["Exposure checks<br/>open databases"] --> N1["nuclei<br/>technology pass"] --> R["Web route<br/>checks"]
end
subgraph MATCH["3 MATCH"]
direction TB
C["CVE correlation"] --> N2["nuclei<br/>AI-targeted pass"]
end
subgraph DECIDE["4 DECIDE"]
direction TB
A["AI triage<br/>and validation"] --> O["Changes, host score,<br/>dashboard, API, alerts"]
end
H["Hygiene<br/>TLS, SPF, DKIM, DMARC, CAA"]
T --> FIND --> PROBE --> MATCH --> DECIDE
DECIDE -.-> H
style FIND fill:#e8f1ff,stroke:#3b82f6,color:#0b3b8c
style PROBE fill:#f1eaff,stroke:#8b5cf6,color:#3b1d8c
style MATCH fill:#fff4e0,stroke:#f59e0b,color:#7a4a00
style DECIDE fill:#e6f7ec,stroke:#22c55e,color:#0b5a2a
linkStyle default stroke:#555,stroke-width:2px
classDef start fill:#111,stroke:#111,color:#fff
classDef step fill:#fff,stroke:#444,color:#111
classDef out fill:#fff,stroke:#16a34a,stroke-width:2px,color:#111
class T start
class D,I,X,N1,R,C,N2,A step
class O out
class H step
Meanwhile the CVE feed runs on its own schedule:
flowchart LR
    F["cve.now feed<br/>and exploitation sources"] --> T{"Tier"}
    T --> FIRE["FIRE"]
    T --> SMOKE["SMOKE"]
    T --> ICE["ICE"]
    FIRE --> M["Match to inventory<br/>product and version"]
    SMOKE --> M
    ICE --> M
    M --> V["AI triage"]
    V --> X["Validate<br/>read-only checks"]
    X --> OUT["Finding<br/>tracked through the API"]

    classDef fire fill:#fee2e2,stroke:#dc2626,color:#7f1d1d
    classDef smoke fill:#fef3c7,stroke:#f59e0b,color:#78350f
    classDef ice fill:#e0f2fe,stroke:#0ea5e9,color:#0c4a6e
    class FIRE fire
    class SMOKE smoke
    class ICE ice
See Pipeline for each stage and Architecture for the services.
Quick start
You need Linux with Docker Engine and the Compose plugin, plus git, make, and python3. 8 GB of RAM and 20 GB of disk are recommended.
git clone https://github.com/hevnsnt/CVEngine.git
cd CVEngine
cp .env.example .env     # set DOMAIN_NAME and replace every change-me
make certs               # HTTPS certificate for the built-in proxy
make up                  # build and start (the first build takes about 30 minutes)
make username            # create your admin account
Open https://<your DOMAIN_NAME>/. Browsers warn about the private certificate authority until you trust secrets/certs/ca.crt. The setup wizard creates your organization and project, offers an optional AI model, and adds your first target. On a fresh Debian or Ubuntu machine, sudo ./install.sh installs Docker and runs these steps for you.
Update with scripts/update.sh, or deploy every new commit automatically (updates). Reverse proxies, backups, and the development stack are in Deployment.
Built for teams and agents
Paste targets grouped by organization and project, and cvENGINE creates the projects for you (organization admins):
##Acme Corp
#Website
example.com
203.0.113.0/28
#Staging
198.51.100.7
Create a token on API tokens and MCP and send Authorization: Bearer <token> to /api/v1/, or connect an MCP client to /mcp/. Tokens use the roles of their user, and read-only tokens are supported. See the Agent API.
Safe by design
- nuclei runs only templates that pass read-only and destination checks, and credentials are never guessed.
- Loopback, link-local, and cloud metadata addresses are never scanned, private ranges stay off until you allow them, and addresses on shared platforms such as CDNs are never port-scanned.
- Injection attempts are blocked, and at the strike threshold the account is disabled and the source IP is blocked for 24 hours.
- Each project's data is isolated, and stored secrets are encrypted.
- Two-step sign-in, an IP allowlist, and an audit log protect access.
Only scan systems you own or are authorized to test.
Documentation
| Doc | What it covers |
|---|---|
| Fire, smoke, and ice | How cvENGINE rates every CVE and why |
| Pipeline | How a target becomes findings |
| Architecture | Services, data, and where AI is used |
| Configuration | Environment variables |
| Deployment | HTTPS, proxies, AI models, backups, dev stack |
| Updates and Upgrade | Staying current |
| Tenancy | Organizations, roles, and two-step sign-in |
| Agent API | REST API and MCP tools |
| Bug bounty | Programs, scope, reports, and submission |
| AI usage | Tracking model calls, tokens, and cost |
| Front end | Design system and pages |
Credits and license
cvENGINE is a fork of reNgine 2.x by Yogesh Ojha and its contributors, and builds on the projects above. See the changelog, contributors, and third-party software.
Released under the GPL-3.0. See LICENSE.
Yorumlar (0)
Yorum birakmak icin giris yap.
Yorum birakSonuc bulunamadi