hexvero
Health Warn
- License — License: MIT
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Low visibility — Only 8 GitHub stars
Code Warn
- process.env — Environment variable access in .github/workflows/release.yml
- fs module — File system access in .github/workflows/release.yml
- fs module — File system access in .github/workflows/review.yml
Permissions Pass
- Permissions — No dangerous permissions requested
No AI report is available for this listing yet.
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
hexvero
Know what changed inside your Electron release.
Diff two builds of an Electron app and see the IPC channels, preload bridge, window settings and network hosts that changed, with file and line on both sides.


Website · Try it · CI · AI agents · Comparison · Limits · Docs
English · Deutsch · Español · Français · Português (Brasil) · Русский · 中文 · 日本語 · 한국어
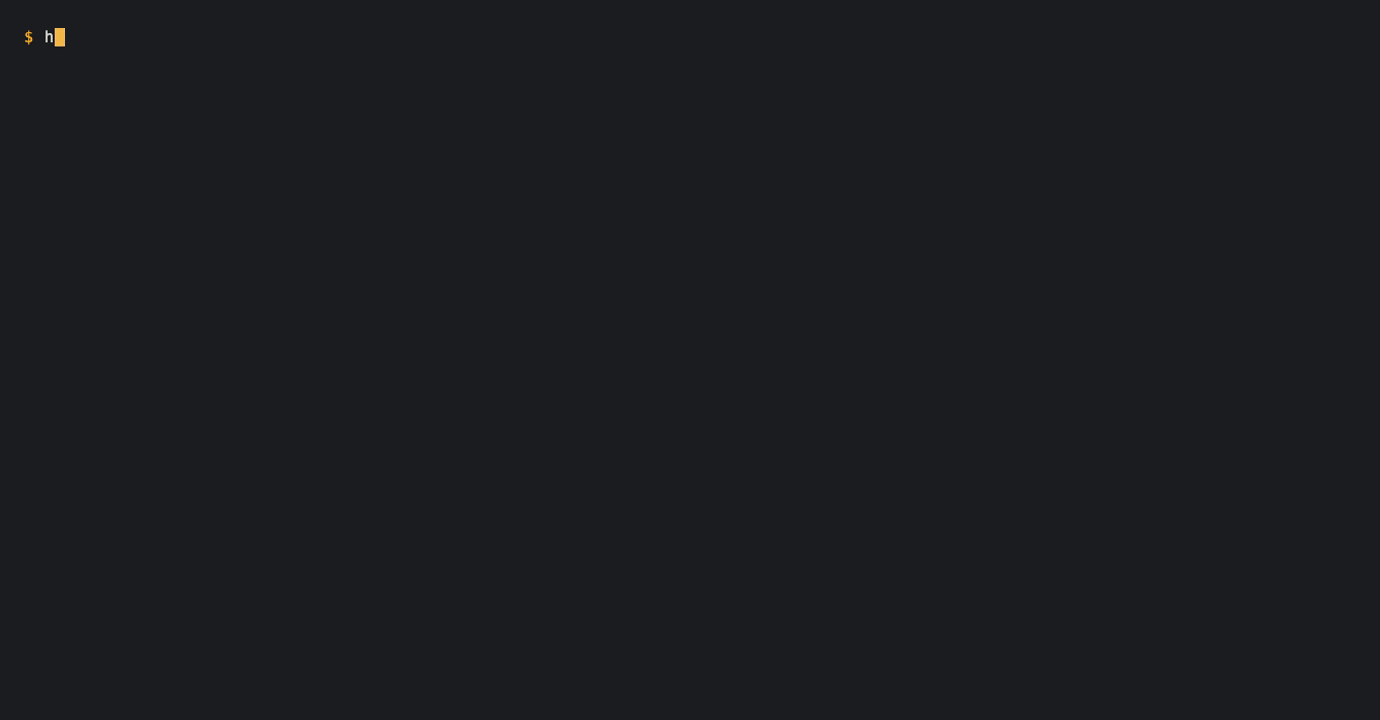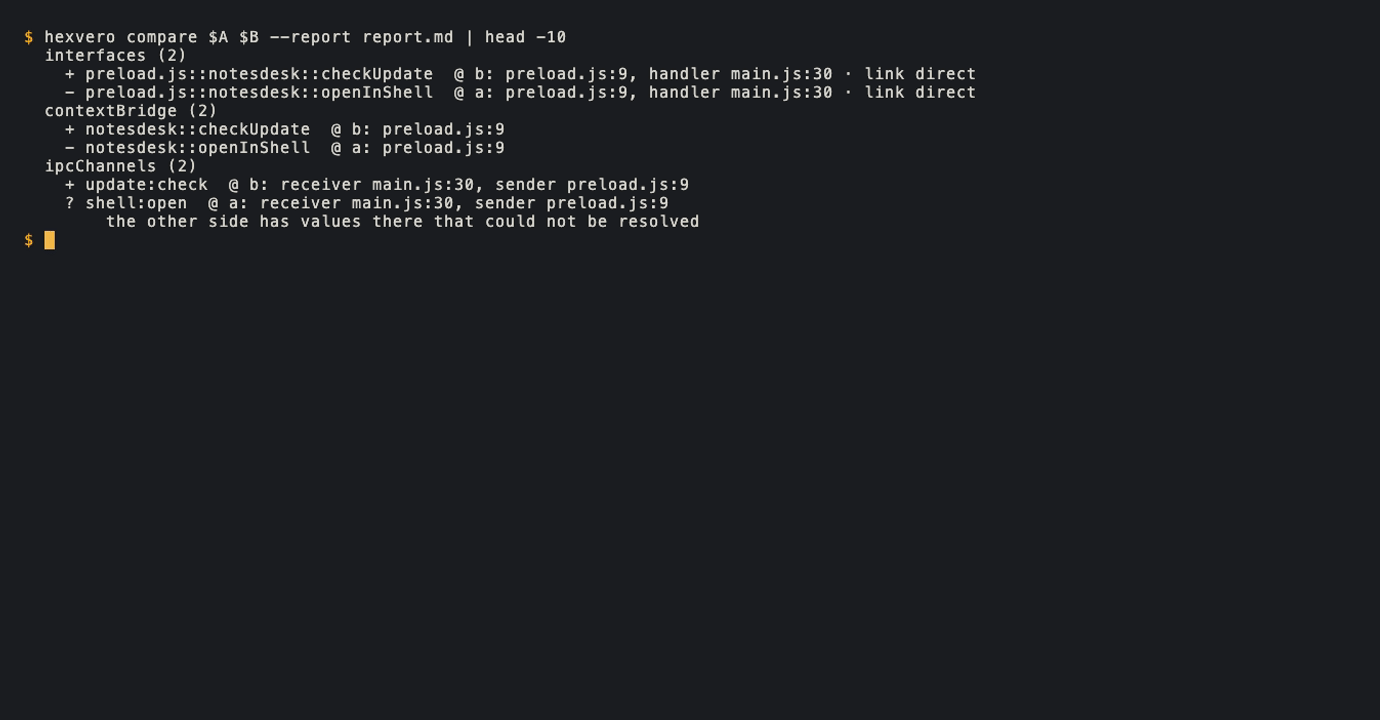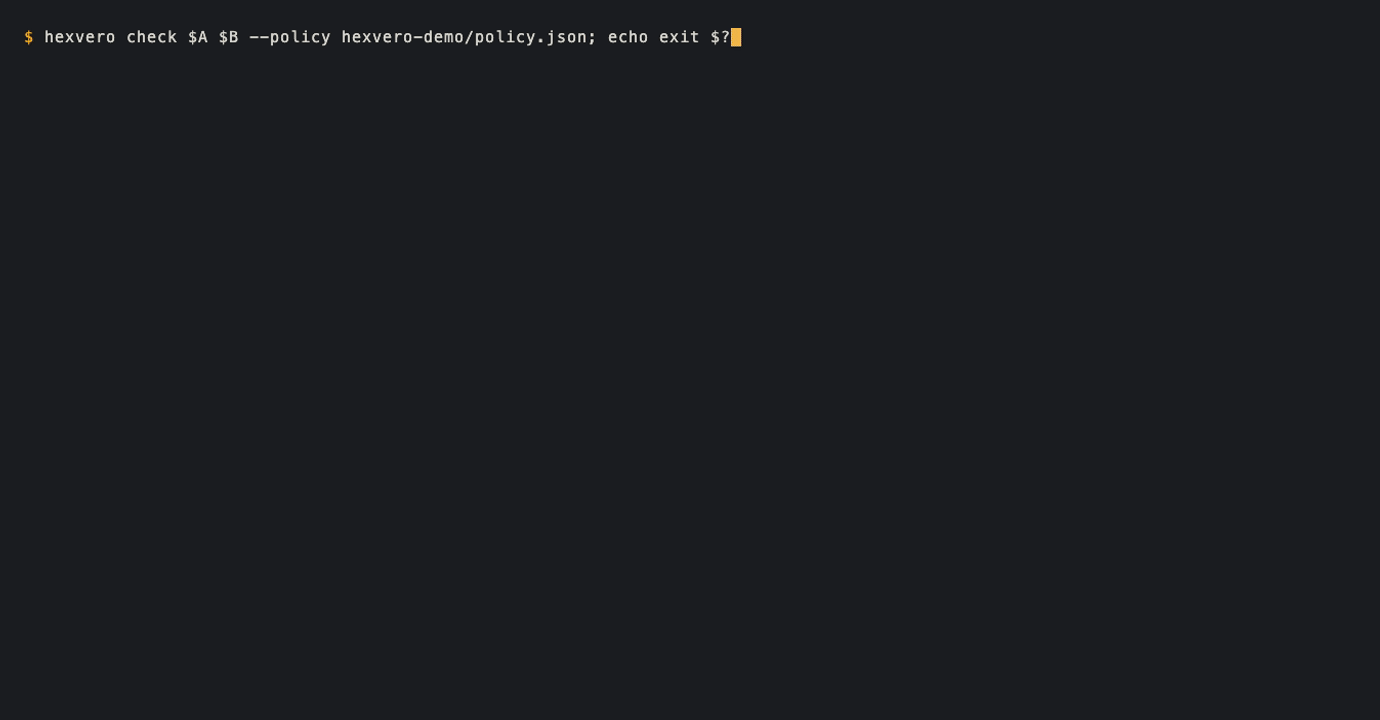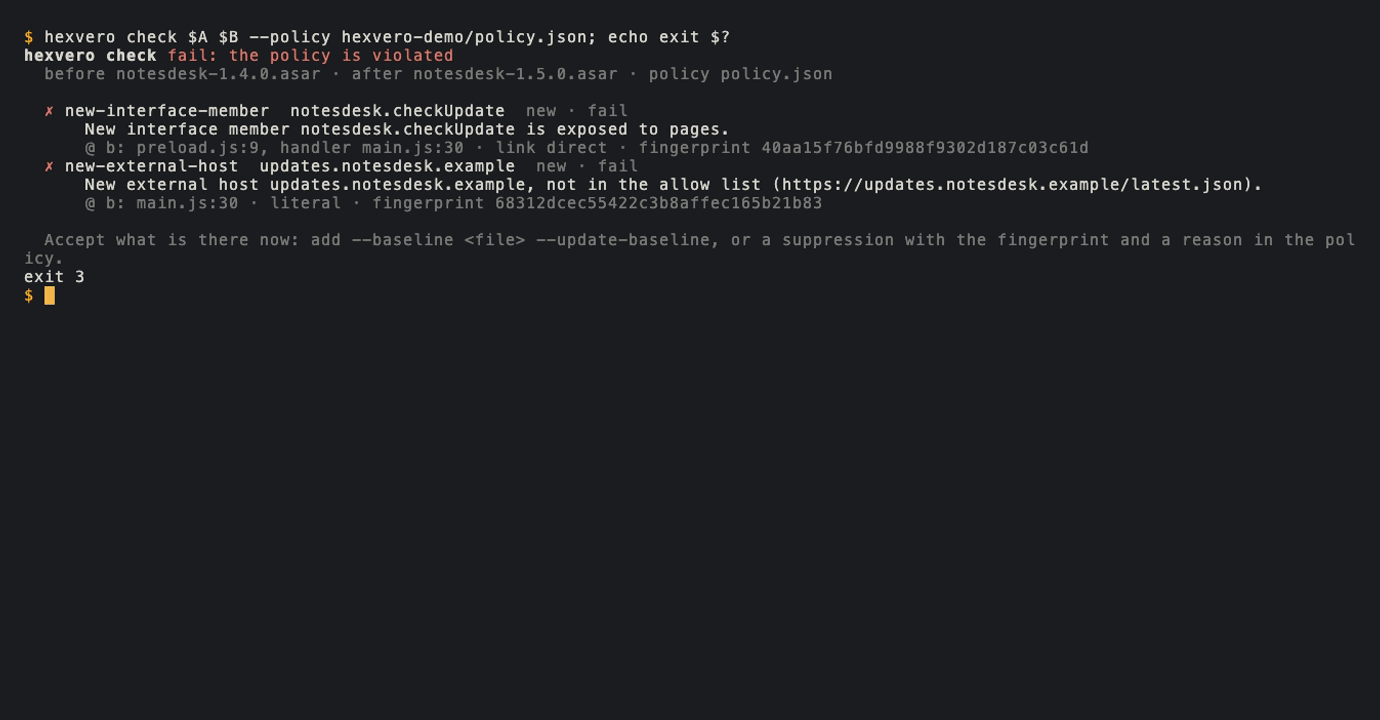
25 seconds, real output · mp4 · recorded with release-gate.tape
Try it in 10 seconds
npx hexvero demo
Needs Node.js 22.12 or newer. It copies two builds of a small example app (NotesDesk 1.4.0 and 1.5.0) into ./hexvero-demo and shows what changed. Excerpt, … marks cuts:
What changed between notesdesk-1.4.0.asar and notesdesk-1.5.0.asar
  Two builds of a small example Electron app, read statically. Nothing was executed.

  interfaces (2)
    + preload.js::notesdesk::checkUpdate  @ b: preload.js:9, handler main.js:30 · link direct
    - preload.js::notesdesk::openInShell  @ a: preload.js:9, handler main.js:30 · link direct
  …
  ipcChannels (2)
    + update:check  @ b: receiver main.js:30, sender preload.js:9
    ? shell:open  @ a: receiver main.js:30, sender preload.js:9
        the other side has values there that could not be resolved
  windows (1)
    ~ main.js::win  @ b: main.js:8
        nodeIntegration: true → false, nodeIntegrationInEffect: "on" → "off", sandbox: false → true
  …
  endpoints (1)
    + main.js::fetch::https://updates.notesdesk.example/latest.json  @ b: main.js:30 · literal
? means hexvero could not tell, so shell:open is reported as unknown, not as removed. Then turn it into a gate:
$ npx hexvero check hexvero-demo/notesdesk-1.4.0.asar hexvero-demo/notesdesk-1.5.0.asar --policy hexvero-demo/policy.json
hexvero check fail: the policy is violated
  ✗ new-interface-member  notesdesk.checkUpdate  new · fail
  ✗ new-external-host  updates.notesdesk.example  new · fail
  …
$ echo $?
3
npx hexvero ui --demo --open shows the same comparison in a local web UI with the source lines of both builds side by side. The full tour: walkthrough.
Why
- A release review asks what the update changed: which channels a page can now reach, which preload members appeared, which window got more permissive, which servers the code now calls.
- A diff of the shipped bundle does not answer that. It is minified JavaScript inside an
app.asar; running the app to find out is not always allowed, and a checklist scanner looks at one build, not the change. - hexvero answers it from the files: each change with the file and line it was read from in both builds, what it could not establish, and a policy that fails CI on a new member, host or more permissive window. Nothing is executed.
What it reads
| IPC and bridge map | window → contextBridge member → IPC channel → ipcMain handler, with how each link was read |
| Window settings | webPreferences per window, and whether nodeIntegration and sandbox are in effect |
| Runtime and fuses | Electron, Chromium and Node versions, fuses and the ASAR integrity record, read from packaged binaries |
| Hosts and storage | network endpoints and localStorage/sessionStorage keys, literal or inferred |
| CI gate and SARIF | hexvero check: exit 0 pass, 3 violated, 4 not decidable; baseline, suppressions, SARIF 2.1.0 |
| MCP for agents | 16 tools with small paged answers, so a coding agent can run the same review |
| Local web UI | the comparison with both builds' source lines side by side, plus an offline HTML report |
Inputs: an app.asar, a macOS .app, a Windows or Linux install directory, or the release .zip you publish. Installers (.dmg, setup .exe, AppImage) need unpacking first. Per-platform paths: docs/cli.md.
On your own app
npx hexvero compare old/YourApp.app new/YourApp.app --report report.html   # one offline HTML page
npx hexvero init old/YourApp.app                                            # starting policy, current hosts allowed
npx hexvero check old/YourApp.app new/YourApp.app --policy .hexvero/policy.json
To accept what is there today, add --baseline .hexvero/baseline.json --update-baseline once; later runs fail only on new findings.
Use it in CI
Pinned to a version so a release cannot change your results unannounced:
jobs:
  hexvero:
    runs-on: ubuntu-latest
    permissions:
      contents: read
    steps:
      - uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7
        with:
          persist-credentials: false
      - uses: actions/setup-node@949feb2413d6458794dcd2491c4babbbce0c15c1 # v7
        with:
          node-version: 24
      # Build your app and fetch the previous release here, e.g. into previous/ and dist/.
      - run: npx --yes [email protected] check previous/app.asar dist/app.asar --policy .hexvero/policy.json
Baseline, Markdown job summary and a least-privilege SARIF upload for code scanning: docs/ci.md.
For AI agents
In Claude Code, server and skill come as one plugin:
/plugin marketplace add maximilianfeix/hexvero
/plugin install hexvero@hexvero
Elsewhere, npx hexvero setup --apply registers the MCP server with the coding agents it finds (dry run without --apply), or run npx -y [email protected] mcp over stdio. Text inside the target is treated as data, never as instructions. Clients, tools and what an agent receives: docs/mcp.md.
How it compares
| hexvero | Electronegativity | REA | diff of two bundles |
|
|---|---|---|---|---|
| Built for | what changed between two builds | known risky patterns in one build | broad reverse engineering, static and dynamic | any text change |
| Compares two builds of one app | yes, list by list | no (one build; checks between Electron versions) | yes (compare_application_versions) |
yes, minified bytes |
Bridge member → IPC channel, blind holdout2 |
65 of 78 | not measured | 6 of 66 | no |
| Release policy with CI exit codes | yes (0/3/4, SARIF) |
SARIF output | not compared | no |
CSP, shell.openExternal, permission handlers |
not yet | yes | not compared | no |
| Status | active, MIT | README: "no longer actively maintaining" | active | n/a |
Electronegativity's README says it is no longer maintained. hexvero covers its use case for release review; parity with its full list of checks is in progress, not shipped. REA does much that hexvero does not (dynamic analysis, devices, decompilers); use it for that. Sources, dates and every caveat: docs/comparison.md.
Accuracy and limits
On the newest blind set, written by someone without access to hexvero, it found 52 of 64 IPC channels with none false, and it misses and misreports rows in other lists (all numbers). It reads files and never runs them, so a finding is what the code contains, not what it does at run time or whether it is exploitable; a passing check is not a security verdict. Parsing a hostile file still processes attacker-controlled bytes, within size, depth and time limits. The full list: docs/accuracy.md.
Docs
Walkthrough · CLI · CI · MCP · Policy schema · Electron rules and sources · Accuracy · Benchmarks · Other formats (native binaries, APK, WebAssembly and more) · Changelog
FAQ: does it run or upload my files?No. Targets are parsed as bytes; nothing is executed. The UI binds to 127.0.0.1 with a per-session token. There is no telemetry and no network call in the code base. Through a cloud-hosted agent, the results that agent requests go to its model provider like any other tool output. Use hexvero only on software you may examine (DISCLAIMER.md).
Contributing
npm install && npm run check      # typecheck, lint, format, unit tests, shape rules
npm run e2e                       # the user flows on real inputs
Rules in CONTRIBUTING.md; good first issue is sized for an afternoon. Found a wrong or missing fact? Open a bug report with hexvero doctor output and, if you can, the file.
If hexvero showed you something you would have missed in a release, a ⭐ helps the next Electron team find it.
License
MIT
Reviews (0)
Sign in to leave a review.
Leave a reviewNo results found