repopilot
Health Gecti
- License — License: NOASSERTION
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Community trust — 23 GitHub stars
Code Uyari
- fs module — File system access in .github/workflows/publish-npm.yml
Permissions Gecti
- Permissions — No dangerous permissions requested
Bu listing icin henuz AI raporu yok.
Local, deterministic review of Git changes: weakened tests and CI gates, security boundaries, blast radius. CLI, GitHub Action, MCP server, and coding-agent plugins.
RepoPilot


Local, deterministic review for Git changes.
RepoPilot helps developers and teams inspect a change before merge. It reports
structural evidence about security boundaries, behavior, local imports and
exports, and the files affected through the dependency graph. The same review
can run from a terminal, in CI, or through an agent integration.
The analysis runs on the machine or CI runner that invokes it. It does not send
source to a hosted service or call an embedded language model. Findings point to
code and explain what to check; reviewers still decide whether a change is safe
for their application.
Example: a change that weakens its own tests
This change drops a range check from applyDiscount. The same change skips the
test that would now fail, removes an assertion from another test, and lets the
CI test step fail without failing the job. Every check that still runs passes.repopilot review . lists them right after its decision:
Decision: REVIEW (Change Proof: REVIEW)
...
Checks this change weakened (details under Review signals):
  ⚑ check gate relaxed — .github/workflows/ci.yml:10
  ⚑ assertions removed — src/pricing.test.ts:5
  ⚑ test skipped — src/pricing.test.ts:9
Further down, each signal explains itself:
    ⚑ check gate relaxed — .github/workflows/ci.yml:10  check step `npm test` in job `test` now has `continue-on-error: true`
    ⚑ assertions removed — src/pricing.test.ts:5  "applyDiscount > takes a percentage off the total": assertions 2 → 1
    ⚑ test skipped — src/pricing.test.ts:9  `it.skip` added on "rejects a discount above 100%"; its result no longer fails the run
These are excerpts of one run (recording). Replay it withscripts/demo-weakened-tests.sh <empty-dir>, then run repopilot review <empty-dir>.
Install and review
cargo install repopilot
# or
npm install -g repopilot

repopilot review . --base origin/main
For uncommitted work, run repopilot review .. The first screen gives onePASS, REVIEW, BLOCK, or NOT ASSESSED decision, its reasons, coverage
limits, and a next action.
A review can surface:
- changes to authentication, request trust, deployment, dependencies, or secret
configuration; - added or removed behavior such as network calls, subprocesses, filesystem
writes, SQL, or error handling; - changed input-to-sink paths, algorithmic structure, or local import/export
contracts; - tests the change stopped running or weakened: committed focus markers such as
it.only, newly skipped tests (it.skip,@pytest.mark.skip,t.Skip,#[ignore]), removed or substituted test cases, tests that lost assertions,
new lint, type, or coverage suppressions, and relaxed CI or tool gates
(continue-on-error,|| true, lowered coverage thresholds, strict mode
off), so a green run cannot hide them; - direct dependents and the wider impact of changed files.
Signals are advisory evidence. For example, a taint-lite signal shows that a
recognized input can reach a recognized sink in the changed source. Confirm the
impact in the context of the application and its configured checks.
Example: review an image-processing change
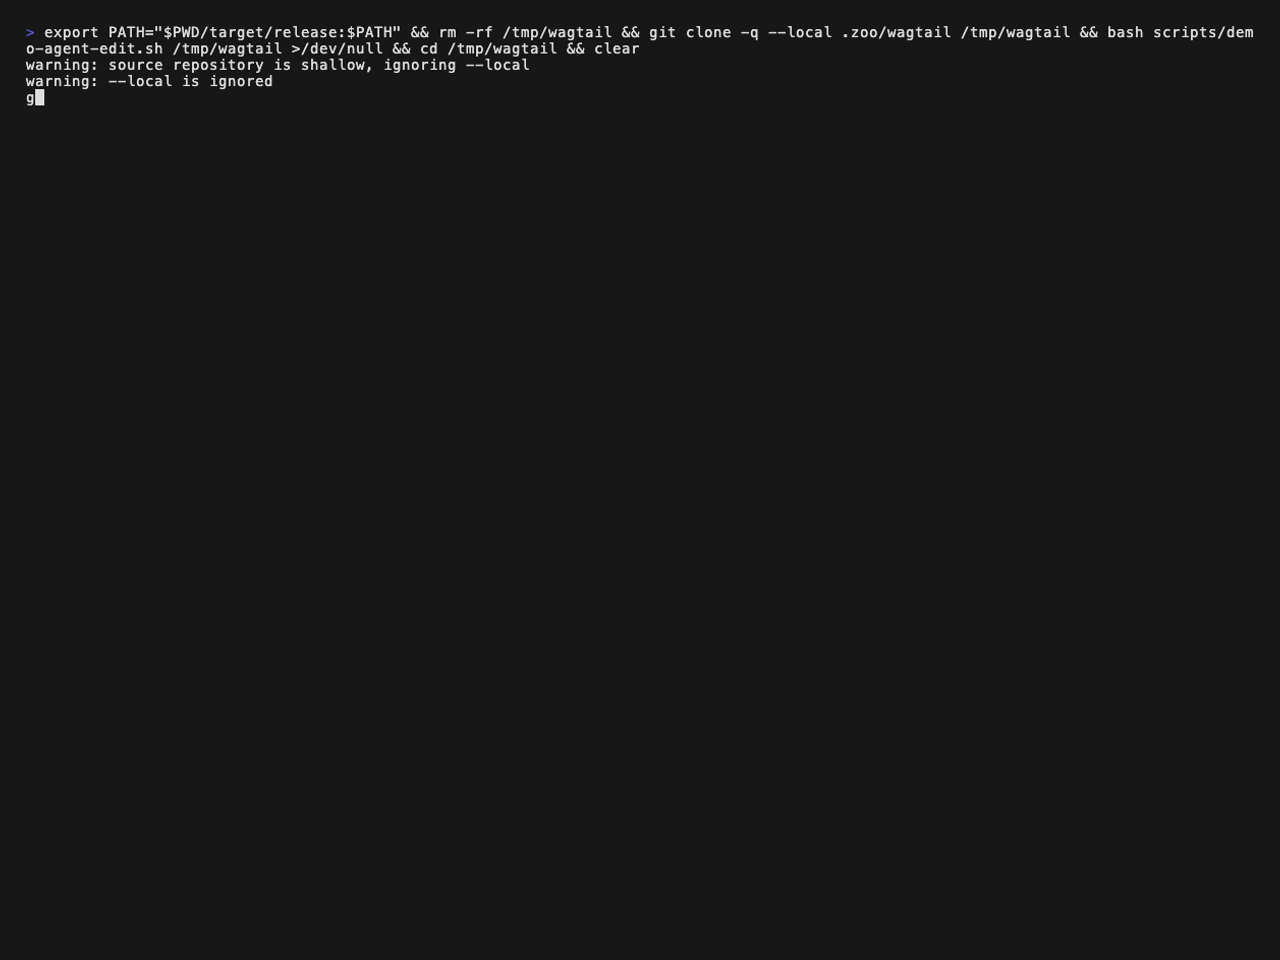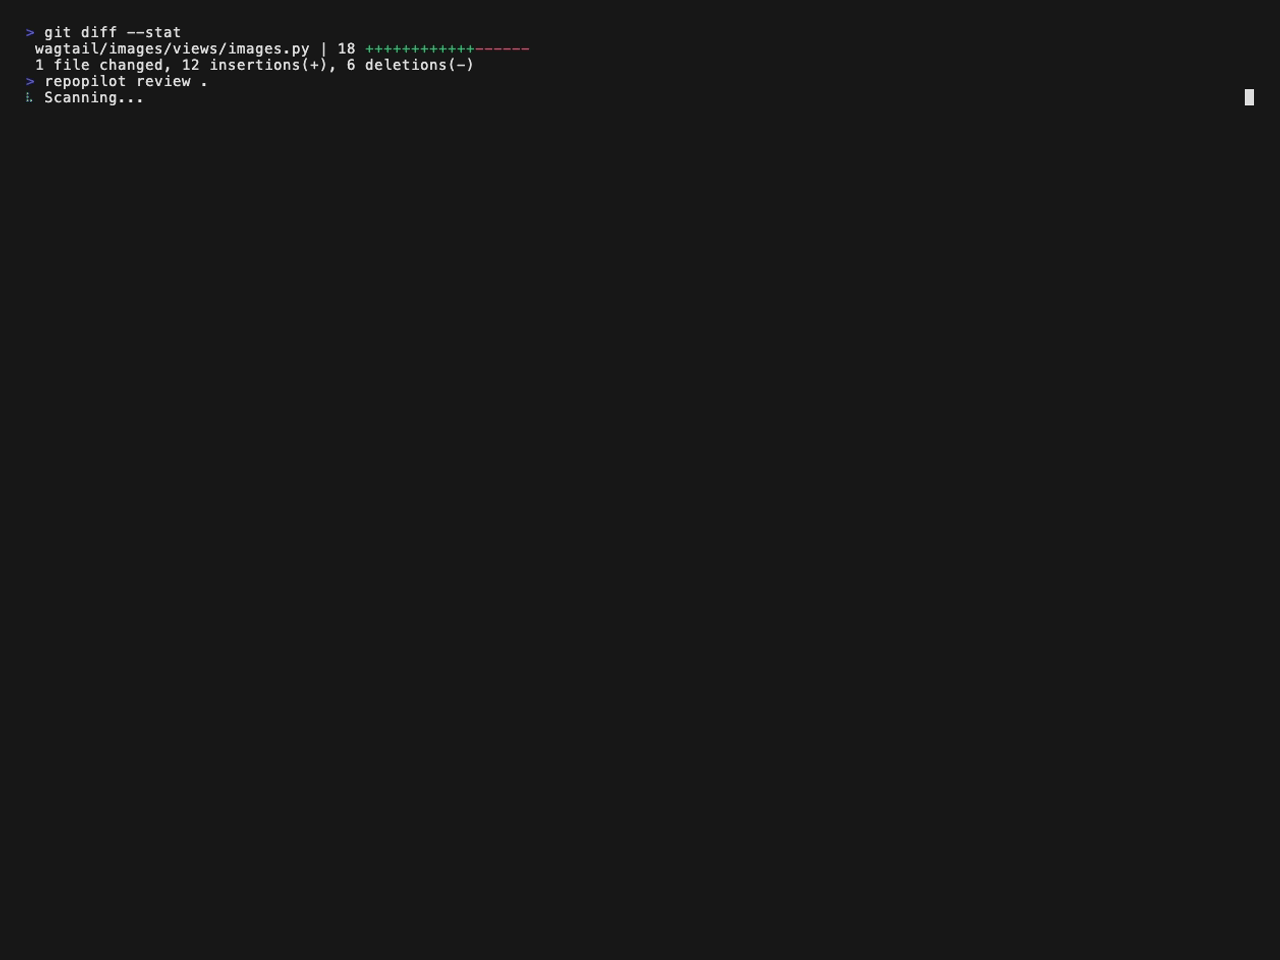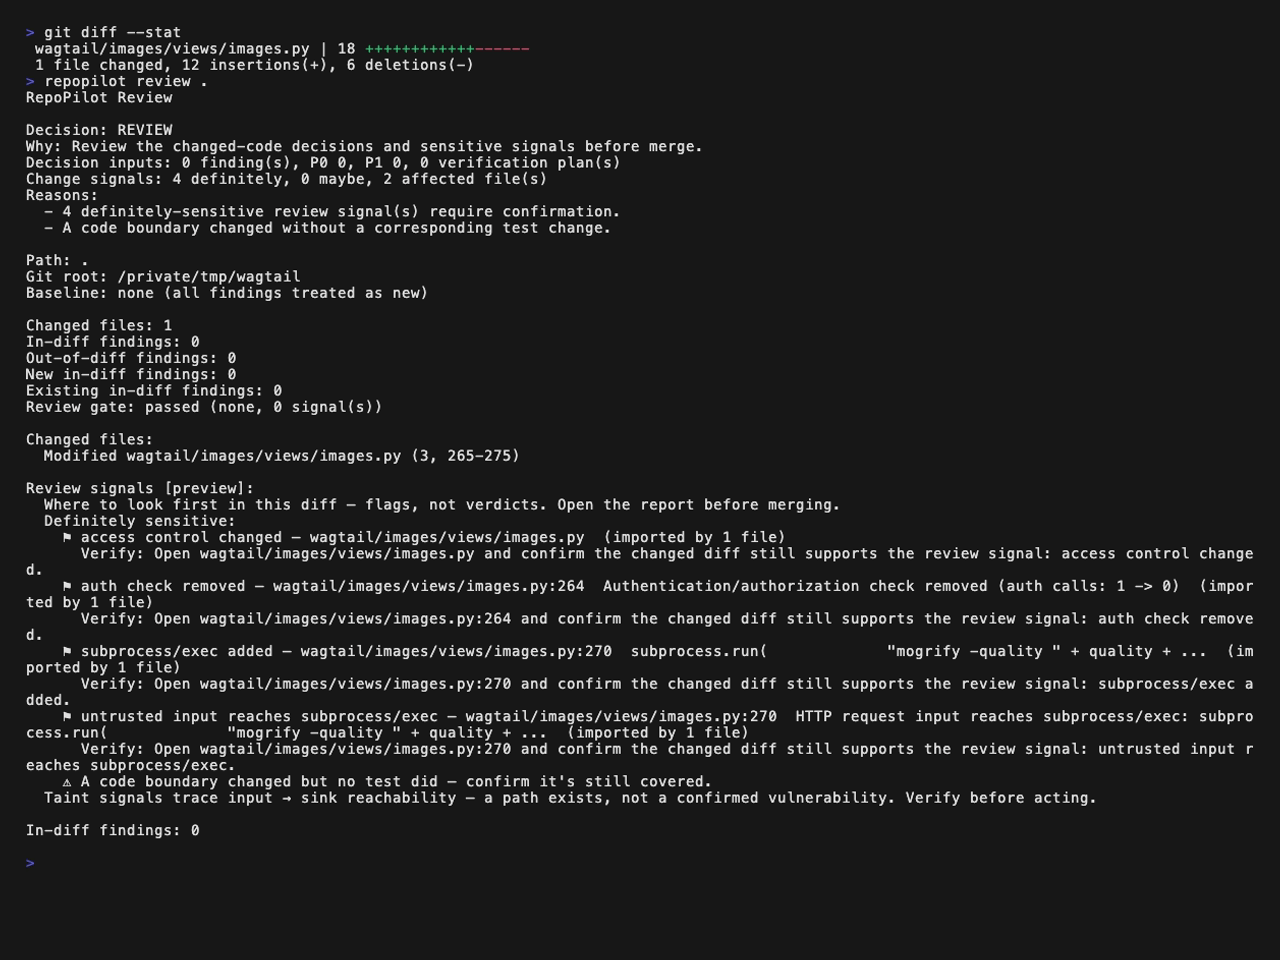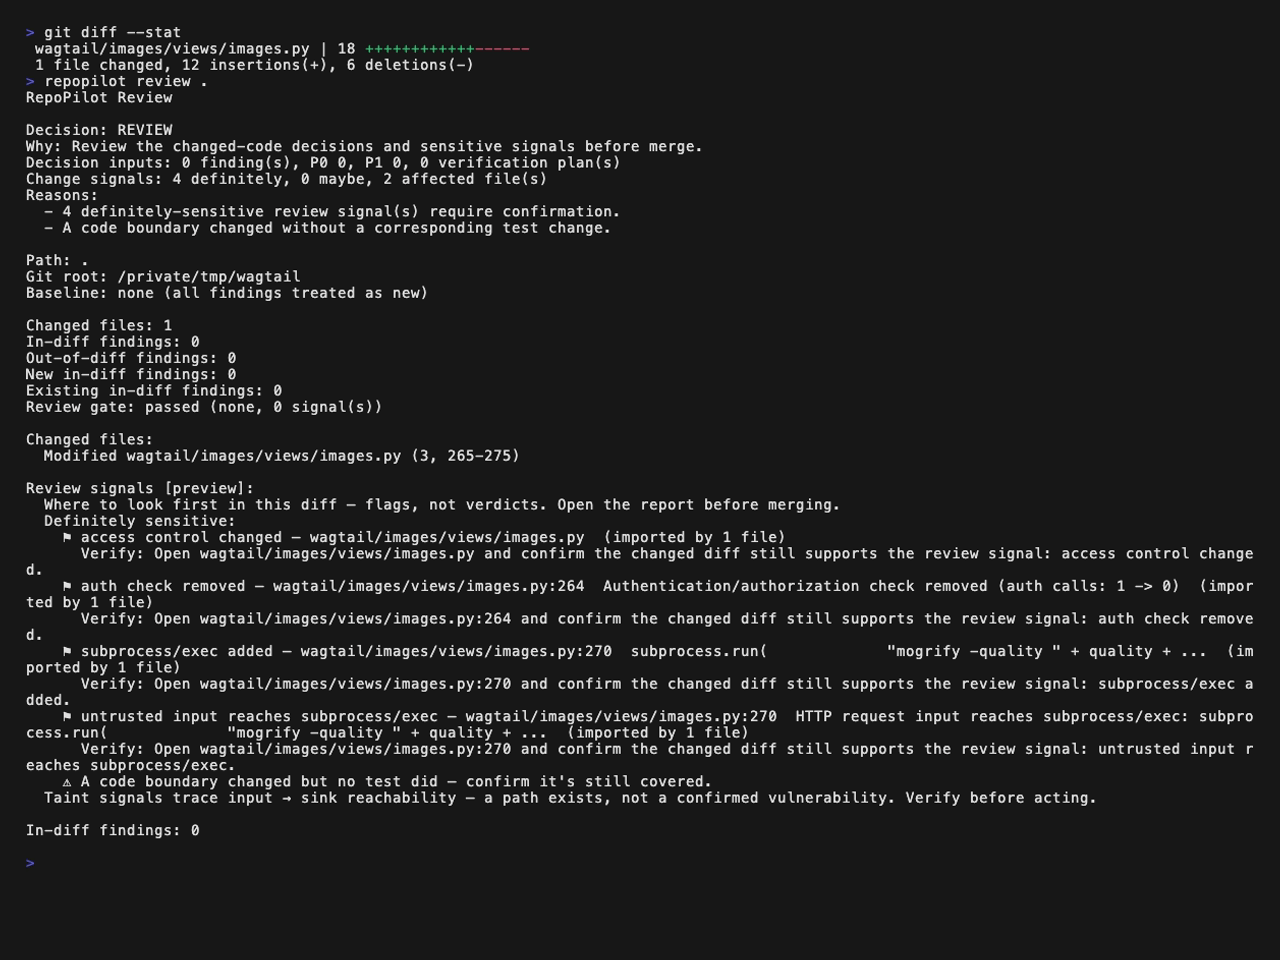
The Wagtail example removes an authorization check and passes request data to a
subprocess in a one-file change. RepoPilot reports both the boundary change and
the input-to-process flow.
Replay the example on the pinned test repository:
python3 scripts/zoo.py clone --only wagtail
scripts/demo-agent-edit.sh .zoo/wagtail
repopilot review .zoo/wagtail
A reported flow is a path to investigate. RepoPilot does not prove that it is
exploitable or that the application is safe.
Use in a team
Gate a branch review on high-confidence signals:
repopilot review . --base origin/main --fail-on-review definitely
A review is VERIFIED only when checks configured for the repository are
explicitly selected with --verify and pass on the reviewed revision. Generate
suggestions for a first setup withrepopilot init --suggestions-output repopilot-suggestions.toml; the file is
separate from active configuration. See configuration.
For a broader repository view, run repopilot scan .. Userepopilot baseline create . to adopt existing findings before gating new work.
Agent and CI integrations
The same review can check work from a human or a coding agent. Record a starting
point and review the changes made since it:
repopilot snapshot
# Work happens here.
repopilot review --since-snapshot
When the working tree is already dirty, the marker also records a baseline
commit of those uncommitted files, so the later review covers only what changed
after the snapshot. It shows what changed, not who changed it.
See common workflows.
In Claude Code, the RepoPilot plugin runs that loop for every session and
stops Claude from finishing while a test it skipped, focused, removed, or
weakened is unexplained:
/plugin marketplace add MykytaStel/repopilot
/plugin install repopilot@repopilot
Codex installs the same plugin (codex plugin marketplace add MykytaStel/repopilot, then codex plugin add repopilot@repopilot). Cursor and
Gemini CLI run the same loop through project hooks. For GitHub Copilot's coding
agent and other agents, RepoPilot provides setup steps, an MCP entry, and anAGENTS.md snippet. See Guard your agent runs.
RepoPilot also provides a local stdio MCP server and a GitHub Action. The MCP
server gives an agent access to the local scan and review tools. The Action runs
RepoPilot on the Actions runner and can publish SARIF or a pull request summary.
See Guard your agent runs, MCP server,
and GitHub integration.
More capabilities
repopilot ai context .creates a local handoff with repository facts,
findings, and a prioritized plan. It makes no model calls.repopilot initcreates configuration or integration files for review.- Reports are available as console, Markdown, JSON, HTML, and SARIF.
Documentation
- Install · Common workflows ·
CLI reference - Current architecture ·
Reports and schemas · Security model - Language support ·
Rules reference · Roadmap - Latest release notes ·
Maintainer documentation
Contributing and development setup: CONTRIBUTING.md.
License
MIT OR Apache-2.0.
Yorumlar (0)
Yorum birakmak icin giris yap.
Yorum birakSonuc bulunamadi