proof-of-stock
Health Gecti
- License — License: MIT
- Description — Repository has a description
- Active repo — Last push 0 days ago
- Community trust — 12 GitHub stars
Code Basarisiz
- rm -rf — Recursive force deletion command in .github/workflows/exam.yml
- fs.rmSync — Destructive file system operation in apps/fault-drills.test.mjs
- network request — Outbound network request in apps/fault-drills.test.mjs
- fs.rmSync — Destructive file system operation in apps/security.test.mjs
- network request — Outbound network request in apps/security.test.mjs
- exec() — Shell command execution in apps/stocks-analytics.mjs
- fs.rmSync — Destructive file system operation in apps/stocks-analytics.mjs
- process.env — Environment variable access in apps/stocks-analytics.mjs
- network request — Outbound network request in apps/stocks-analytics.mjs
- fs.rmSync — Destructive file system operation in apps/stocks-analytics.test.mjs
- process.env — Environment variable access in apps/stocks-analytics.test.mjs
- network request — Outbound network request in apps/stocks-analytics.test.mjs
Permissions Gecti
- Permissions — No dangerous permissions requested
Bu listing icin henuz AI raporu yok.
Checks if a tokenized-stock contract is on the issuer's own registry, with the issuer price and the on-chain gap.
Proof of Stock™


At a glance
Is this stock token the real one? Paste an address or a ticker; we check it against the issuer's own list on Base
(Coinbase) and Robinhood Chain (Robinhood).
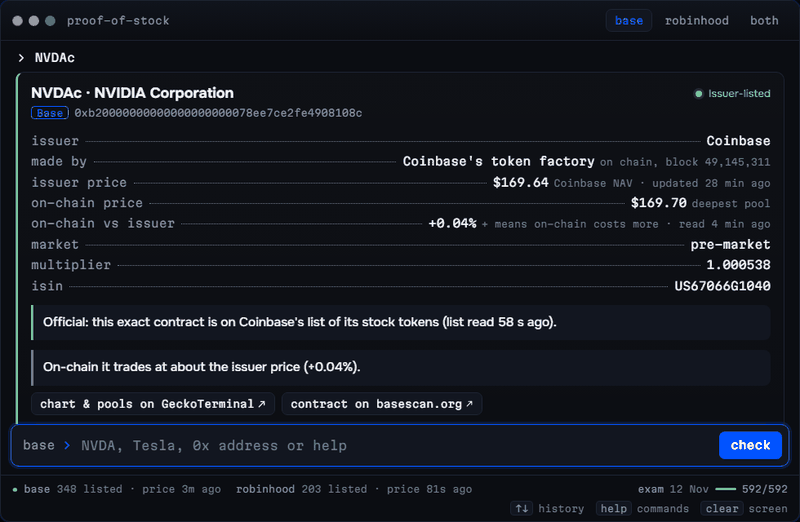 A token passport. NVDAc on Base, on Coinbase's list. |
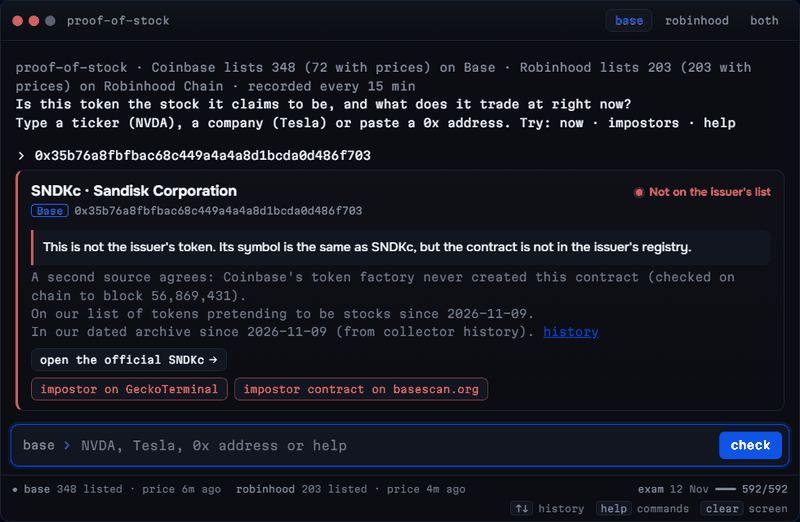 An impostor. Calls itself SNDKc; not on the issuer's list. |
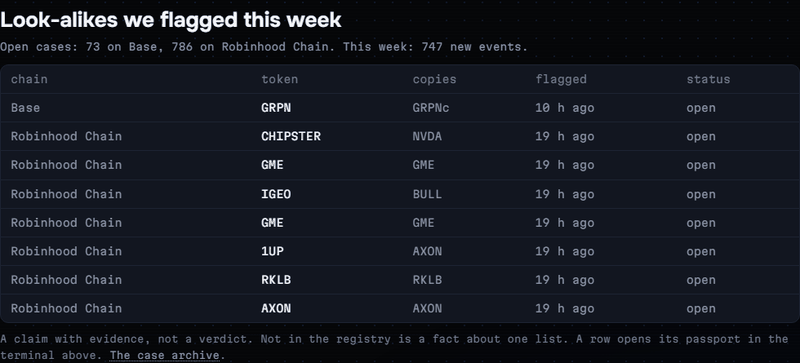 Look-alikes flagged. The weekly list; the archive is at /history. |
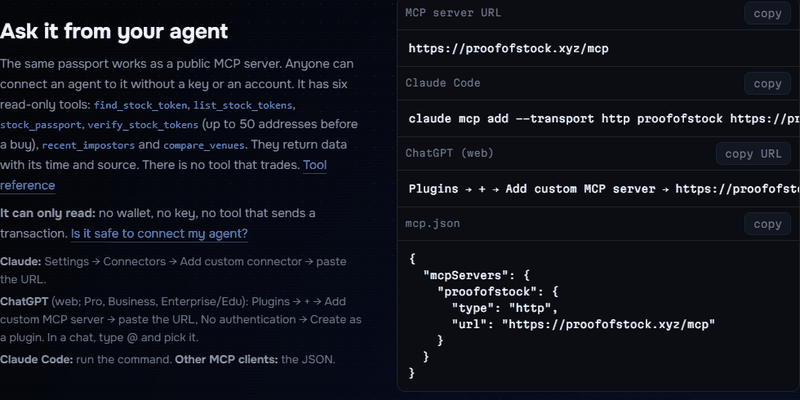 Ask it from your agent. A public MCP server, no key. |
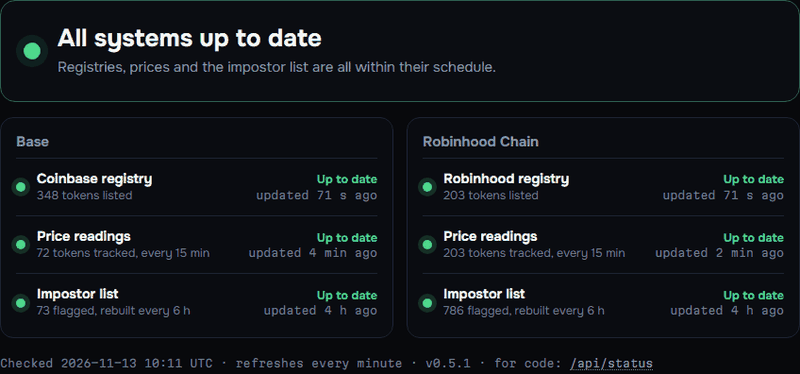 Status. How fresh each registry, price and list is. |
Links Site · Passport · /verify · /history · /status · /anchors · Docs MCP https://proofofstock.xyz/mcpMCP registry xyz.proofofstock/proof-of-stockContact [email protected] |
Proof of Stock tells you whether a tokenized-stock contract is the issuer's own. It looks the exact address up in the
issuer's registry: Coinbase's for Base, Robinhood's for Robinhood Chain. A name or a symbol proves nothing, so tokens
that copy a listed symbol are flagged and pointed at the listed contract.
For a listed token it also shows the issuer's price, how old that price is, and how far the deepest on-chain pool
trades from it.
It is for:
- people buying stock tokens, who want to check a contract before they buy;
- agent builders, whose agents need the same check before a swap.
Live at proofofstock.xyz. Documentation: proofofstock.xyz/docs.
Use it
No key and no sign-up for any of these.
| Site | proofofstock.xyz: paste an address or type a ticker. |
| MCP server | https://proofofstock.xyz/mcp (Streamable HTTP, stateless). Six tools: find_stock_token, list_stock_tokens, stock_passport, verify_stock_tokens, recent_impostors, compare_venues. |
| JSON API | GET /verify, GET /badge.svg, GET /api/passport and more. See the HTTP API reference. |
| Guard | @proofofstock/guard, a pre-trade check for Node agents, with a Coinbase AgentKit action. npm install @proofofstock/guard, no dependencies. It lives in packages/proofofstock-guard. |
Add the MCP server to Claude Code:
claude mcp add --transport http proofofstock https://proofofstock.xyz/mcp
Claude, ChatGPT, Cursor and raw JSON-RPC are covered in the tutorial.
Check us, not just our answers
A checker is worth something only if you do not have to take its word. Each of these works without trusting us:
- The list behind a verdict. Every answer names the issuer list it was decided against by the SHA-256 of its
sorted addresses, with a shell command that computes the same hash from the issuer's own API, and a URL of that
exact list frozen. - A receipt to keep.
/verify?...&receipt=1returns a record of the check thatscripts/receipt-check.mjscan check again months later, after the issuer's list has
changed. See Keep a receipt of a check. - The issuer's factory, read from the chain. Each issuer creates its tokens from a factory that logs every one.
We read those logs as a second source (issuer_factoryin each answer, with the block and the transaction), so a
verdict never rests on the issuer's HTTP list alone. The health check alerts if a listed token was never created by
that factory. Today's counts are on the status page. - Prices you can replay. An on-chain price carries its block and the exact call;
eth_callat that block returns
the same bytes. - A public exam, every day. Every token on the issuers' lists, plus the week's look-alikes, strangers and tokens asked on the wrong chain: questions whose right answer comes from the issuers, not from us. The reports are in the
exambranch. - An outside check every 30 minutes. It runs on GitHub's own runners, not on our host: it hashes each issuer's
list straight from the issuer against ourlist_proof, and calls a passport's on-chain price evidence again at its
block for the same bytes (scripts/canary.mjs). - History anchored in Bitcoin. Once a day, a manifest of every data file of the day is timestamped through
OpenTimestamps. See Check that our data existed on a given day.
Example
Check one address on Base. This one calls itself SNDKc but is not on Coinbase's registry:
curl -s 'https://proofofstock.xyz/verify?chain=base&address=0x35b76a8fbfbac68c449a4a4a8d1bcda0d486f703' \
  | jq '{listed, impostor, listed_on_other_chain, registry_age_s}'
{
  "listed": false,
  "impostor": { "kinds": ["registry_symbol"], "imitates_symbol": "SNDKc", "listed_address": "0xb200000000000000000000397293cb8cda9a10c5" },
  "listed_on_other_chain": null,
  "registry_age_s": 112
}
listed is true only when this exact address is in the registry. impostor.listed_address is the contract the issuer
actually lists. A 503 means the registry could not be read: that is no answer, not "not listed". More in
Check a contract before listing or buying it.
What it does not do
- It only reads. It never trades, has no accounts and no cookies, and holds no wallet. Its one key lives on our own server and writes our daily anchor hash to Base and Robinhood Chain, from its own address, value zero; it can do nothing else, and nothing you send can make it sign.
- It is not advice. An answer is a fact about data at a stated time. See Legal.
- "Not listed" is not "fake". A genuine token of another issuer answers the same. Only Coinbase on Base and
Robinhood on Robinhood Chain are checked. - It is not a live quote. On-chain prices are recorded every 15 minutes, and every answer says how old it is.
- It is not affiliated with Coinbase or Robinhood. Their names and tickers are their trademarks.
How the answers are computed, and the known limits: Methodology.
Run the tests
Node 20 or later.
npm install
npm test        # every suite, no network
npm run locks   # mutation locks: each breaks the code on purpose and needs a test to go red
To run the site locally, point it at the recorder's data and open 127.0.0.1:3005:
STOCKS_ROOT_BASE=<dir> STOCKS_ROOT_ROBINHOOD=<dir> npm start
The recorder (scripts/stocks/stock-peg.mjs --chain=base --root=<dir>) needs outbound HTTPS to the issuer APIs,
DexScreener and GeckoTerminal.
Layout
| Path | What |
|---|---|
evm/core/stocks/ |
the logic, with no I/O: registries, impostors, premium, pool rules, NYSE calendar, passport, verify |
apps/ |
the site, the JSON API and the MCP server |
packages/proofofstock-guard/ |
the guard |
scripts/stocks/ |
the recorder (every 15 min), the impostor list (every 6 h), CLIs |
schemas/v2/ |
schemas of the recorded rows, checked on every write |
tests/locks/ |
the mutation locks |
deployment/ |
the nginx and systemd units the live site runs on |
docs/ |
the documentation served at proofofstock.xyz/docs |
Licence, security, contact
- Code under the MIT licence.
- The name is not the code. "Proof of Stock", the domain proofofstock.xyz and the badge are trademarks of the
project's owner and are not covered by that licence. Fork the code, run it, sell what you build with it. What you
may not do is publish it under this name or badge, or let a reader think an answer came from here when it did
not: the whole point of this service is that a verdict can be traced to who made it. - Found a vulnerability? See SECURITY.md. Please do not open a public issue for it.
- Contact: [email protected].
- What changed in each release: CHANGELOG.md.
Yorumlar (0)
Yorum birakmak icin giris yap.
Yorum birakSonuc bulunamadi